What is an ISMS? The information security management system explained
What is an ISMS? It is a management system for information security, not a piece of software and not a certificate. See what ISO 27001:2022 requires clause by clause, where NIS2, DORA and GDPR come in, and how to build one.

Ask ten people "what is an ISMS?" and you'll get ten answers. A software tool. A folder of policies. The ISO 27001 certificate on the wall. A project the IT department ran two years ago.
None of those is wrong exactly, but none is the whole thing either. That confusion matters, because customers, auditors and now regulators ask for evidence that information security is managed, not just that a few controls exist.
This guide answers the question "what is an ISMS?" properly. You get the definition, the ISO/IEC 27001:2022 requirements clause by clause, the EU and UK law that expects the same work, a worked example and an honest list of what an ISMS will not do for you.
The short answer: what is an ISMS?
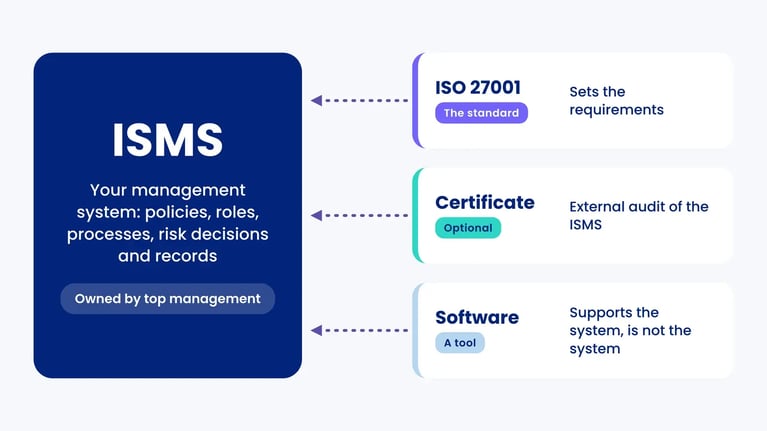
ISMS stands for information security management system. It is the set of policies, roles, processes, risk decisions and records an organisation uses to protect the confidentiality, integrity and availability of its information, and to keep improving that protection over time.
The internationally recognised requirements for an ISMS are in ISO/IEC 27001:2022. The standard does not tell you which firewall to buy. It tells you how to decide, document, check and improve, with top management accountable for the result.
Three things an ISMS is not:
- It is not software. You can run an ISMS in documents and spreadsheets or in a platform. The tool supports the system, it isn't the system.
- It is not a certificate. Certification is an optional external audit of your ISMS against ISO 27001.
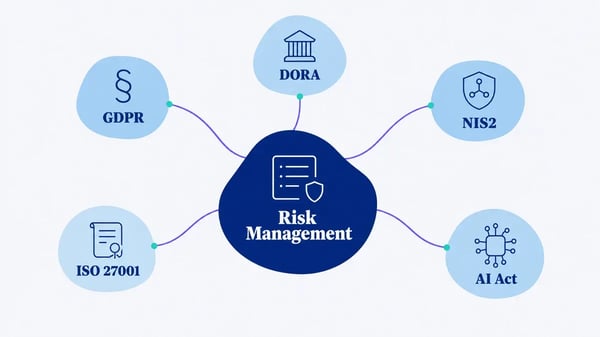
- It is not a law. No EU regulation says "you must have an ISMS", but NIS2, DORA and GDPR all require the kind of risk-based, documented and reviewed security management that an ISMS delivers.
ISMS meaning, full form and definition
The ISMS full form is information security management system. The word that does the heavy lifting is "management". An ISMS is a management system in the same family as ISO 9001 for quality and ISO 14001 for the environment, and it follows the same harmonised clause structure.
A workable ISMS definition, based on the ISO/IEC 27000 series, is this: a systematic approach to establishing, implementing, operating, monitoring, reviewing, maintaining and improving an organisation's information security, based on a risk approach. The overview standard ISO/IEC 27000 was reissued in July 2026 as a sixth edition, now focused on concepts and on how the 27000 family fits together rather than on terminology.
Because search results mix these terms freely, it helps to separate them before going further:
| Term | What it is | Who decides | Mandatory? |
|---|---|---|---|
| ISMS | Your organisation's management system for information security | Your top management | Not by name, but the underlying work is required by several laws |
| ISO/IEC 27001:2022 | The international standard with the requirements for an ISMS (clauses 4-10 plus Annex A) | ISO and IEC | Voluntary, unless a contract, tender or national rule requires it |
| ISO 27001 certification | A third-party audit confirming that a defined scope of your ISMS conforms to the standard | An accredited certification body | Voluntary |
| ISO/IEC 27002:2022 | Guidance on how to implement the 93 controls | ISO and IEC | Guidance only, not certifiable |
| ISMS software | A tool for documenting risks, controls, tasks and evidence | You choose it | No |
| Security controls | The concrete measures (MFA, backups, training, door locks) the ISMS selects and monitors | Your risk assessment | Depends on your risks and legal duties |
If you want the wider distinction between the two disciplines behind all this, our article on the difference between cybersecurity and information security covers it.
What an ISMS is made of: ISO 27001:2022 clause by clause
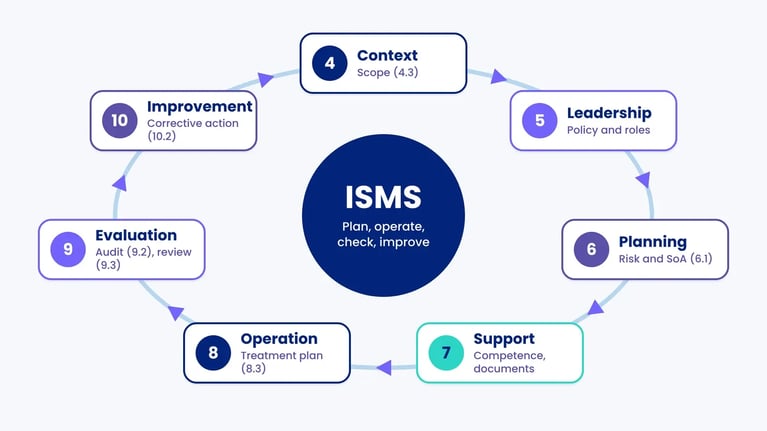
ISO/IEC 27001:2022 was published in October 2022, and Amendment 1:2024 added climate change as an issue organisations must consider when they determine their context. The requirements sit in clauses 4 to 10. Clauses 0 to 3 are introduction, scope, references and terms, and contain no requirements.
| Clause | What it requires | What an auditor will ask to see |
|---|---|---|
| 4 Context | Internal and external issues (4.1), interested parties and their requirements (4.2), the ISMS scope (4.3) | A documented scope statement with boundaries and interfaces |
| 5 Leadership | Top management commitment (5.1), an information security policy (5.2), assigned roles and authorities (5.3) | A signed policy and a clear owner for the ISMS |
| 6 Planning | Risk assessment process (6.1.2), risk treatment process and Statement of Applicability (6.1.3), security objectives (6.2), planning of changes (6.3) | Risk criteria, a risk register, a treatment plan, the SoA and measurable objectives |
| 7 Support | Resources (7.1), competence (7.2), awareness (7.3), communication (7.4), documented information (7.5) | Training records and version-controlled documents |
| 8 Operation | Operational planning and control (8.1), risk assessments at planned intervals (8.2), implementing the treatment plan (8.3) | Evidence that the plan was carried out, not just written |
| 9 Performance evaluation | Monitoring and measurement (9.1), internal audit (9.2), management review (9.3) | An audit programme, audit reports and management review minutes |
| 10 Improvement | Continual improvement (10.1), nonconformity and corrective action (10.2) | A log of nonconformities with root cause and follow-up |
The risk engine: clauses 6.1.2, 6.1.3 and the Statement of Applicability
Everything in an ISMS hangs off the risk assessment. Clause 6.1.2 requires you to set risk acceptance criteria, identify risks to confidentiality, integrity and availability, give each risk an owner, and analyse and evaluate them in a way that produces consistent, comparable results.
Clause 6.1.3 then requires a treatment decision for each risk, a comparison of your chosen controls against Annex A so nothing necessary is overlooked, and a Statement of Applicability (SoA). The SoA lists every Annex A control, whether it's included, why, and whether it's implemented. Risk owners must approve the treatment plan and accept the residual risk.
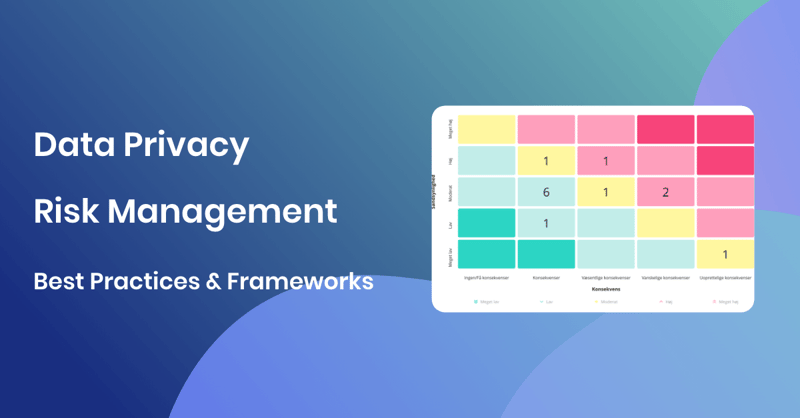
Our guide to information security risk management goes deeper into methods, and the article on the risk assessment matrix covers the scoring tool most organisations start with.
Annex A: 93 controls in four themes
The 2022 edition cut the control set from 114 to 93 and regrouped it into four themes. Eleven controls are new, among them threat intelligence (A.5.7), information security for cloud services (A.5.23), ICT readiness for business continuity (A.5.30), data masking (A.8.11) and secure coding (A.8.28).
| Theme | Controls | Examples |
|---|---|---|
| A.5 Organisational | 37 | Security policies (A.5.1), asset inventory (A.5.9), supplier relationships (A.5.19-A.5.22), incident management planning (A.5.24), legal and contractual requirements (A.5.31) |
| A.6 People | 8 | Screening (A.6.1), awareness and training (A.6.3), remote working (A.6.7) |
| A.7 Physical | 14 | Physical entry controls such as badge or biometric access (A.7.2), physical security monitoring (A.7.4) |
| A.8 Technological | 34 | Privileged access (A.8.2), secure authentication (A.8.5), vulnerability management (A.8.8), backup (A.8.13), logging (A.8.15), use of cryptography (A.8.24) |
A common mistake is to treat Annex A as a checklist to be completed. It isn't. You may exclude a control if your risk assessment and legal duties don't call for it, as long as the SoA says why. And a biometric door reader belongs to the physical theme, not the technological one, even though it runs on software.
Where did Plan-Do-Check-Act go?
Many articles describe the ISMS as a PDCA cycle. The 2005 edition of ISO 27001 built its structure around PDCA explicitly. The 2013 and 2022 editions dropped that requirement, and clause 10.1 now simply demands continual improvement of the ISMS's suitability, adequacy and effectiveness. PDCA is still a useful mental model. It just isn't something an auditor will check for by name.
What the law requires, and where an ISMS fits
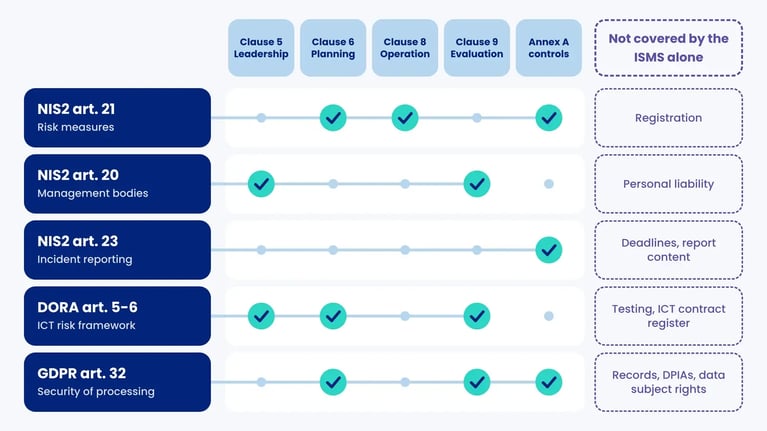
Once the question "what is an ISMS?" is settled, the next one is usually whether you are legally obliged to have one. EU law is technology-neutral and rarely names a standard. What it does require, again and again, is the core ISMS loop: assess risk, choose proportionate measures, document them, test whether they work and report to management.
| Law | Provision | What it requires | ISMS element that delivers it | What the ISMS won't cover on its own |
|---|---|---|---|---|
| NIS2 Directive (EU) 2022/2555 | Art. 21(1)-(2) | Appropriate and proportionate risk management measures based on an all-hazards approach, covering at least ten areas, from (a) risk analysis policies to (j) multi-factor authentication | Clauses 6.1.2-6.1.3, 8 and Annex A | Registration with the national authority |
| NIS2 | Art. 20 | Management bodies approve the measures, oversee implementation, can be held liable and must follow training | Clauses 5.1 and 9.3 | Personal liability rules under national law |
| NIS2 | Art. 23 | Early warning within 24 hours, incident notification within 72 hours, final report within one month for significant incidents | A.5.24-A.5.28 incident management | The regulatory deadlines and report content |
| DORA (EU) 2022/2554 | Art. 5-6 | Management body accountable for ICT risk, a documented ICT risk management framework reviewed at least once a year | Clauses 5, 6, 9.3 | DORA-specific testing, registers of ICT contracts and incident classification |
| GDPR (EU) 2016/679 | Art. 32(1) | Security appropriate to the risk, including a process for regularly testing and evaluating the effectiveness of measures (art. 32(1)(d)) | Clauses 6.1.2, 9.1, 9.2 and A.5.34 | Records of processing (art. 30), DPIAs (art. 35), lawful basis and data subject rights |
The NIS2 security measures are made concrete for digital infrastructure providers, such as cloud, data centre and managed service providers, by Implementing Regulation (EU) 2024/2690. In June 2025 ENISA published its technical implementation guidance for that regulation, mapping each requirement to ISO/IEC 27001:2022, ISO/IEC 27002:2022 and NIST CSF 2.0. That is as close to official confirmation as you'll get that an ISO 27001 ISMS is a sound base for NIS2. For the full gap analysis, see NIS2 vs ISO 27001.
National implementation still varies
NIS2 had to be transposed by 17 October 2024. On 8 July 2026 the European Commission referred Ireland, Spain, France and the Netherlands to the Court of Justice for failing to transpose it in full. Most other member states have national laws in force. Denmark, for instance, has applied its NIS2 act since 1 July 2025, and Danish state authorities have had to manage information security according to ISO 27001 since 2016, according to the Danish Agency for Digital Government.
For a group operating in several countries, an ISMS is the practical way to absorb that variation. The risk method, controls and evidence stay the same, and only the registration and reporting layer changes per country.
The UK position
NIS2 does not apply in the UK. UK operators remain under the NIS Regulations 2018, and the Cyber Security and Resilience (Network and Information Systems) Bill was at report stage in the House of Lords in September 2026, with no Royal Assent yet. UK GDPR keeps the same article 32 security duty. UK organisations that serve EU customers in NIS2 sectors will still meet NIS2 expectations through supplier questionnaires and contracts.
Cyber Essentials, the UK government-backed scheme, is sometimes mistaken for an ISMS. It certifies five technical controls (firewalls, secure configuration, user access control, malware protection and security update management). That's a useful baseline, but there's no risk assessment, internal audit or management review.
Who needs an ISMS?
Strictly speaking, nobody is required to have something called an ISMS unless a contract or national rule says so. In practice, you need one if any of these apply:
- You are an essential or important entity under NIS2, or a financial entity under DORA.
- You supply NIS2 or DORA entities. They must manage supply chain security under NIS2 art. 21(2)(d) and ICT third-party risk under DORA, and they pass those expectations down to you.
- You process personal data at a scale where "appropriate measures" under GDPR art. 32 has to be demonstrable, not just asserted.
- Customers or tenders ask for ISO 27001 certification or an assurance report.
Uptake is growing fast. The ISO Survey 2024 counted 96,709 valid ISO/IEC 27001 certificates covering 179,877 sites worldwide, roughly double the 2023 figure. The survey notes that the 2023 data was incomplete, which exaggerates the jump. The ISO Survey is published each autumn, so check for the 2025 figures.
How an ISMS works in practice: a worked example
The clearest answer to "what is an ISMS?" is to watch one work on a single risk.
Harbourline Systems and Priya Nair are fictional. We invented them for this article.
Harbourline Systems is a 180-employee managed service provider. It runs a remote monitoring and management (RMM) tool that has administrative access to around 60 customer networks. Priya Nair, head of security and compliance, owns the ISMS.
1. Scope (clause 4.3). Priya scopes the ISMS to managed services, the service desk and the supporting cloud platform. Internal HR systems are outside the certification scope but still covered by the security policy. She writes that down, because a narrow scope is one of the first things a customer should check on a certificate.
2. Risk criteria (6.1.2). Management approves a 5x5 matrix. Any risk scoring 12 or more needs treatment, and anything above 8 needs a named owner's signed acceptance.
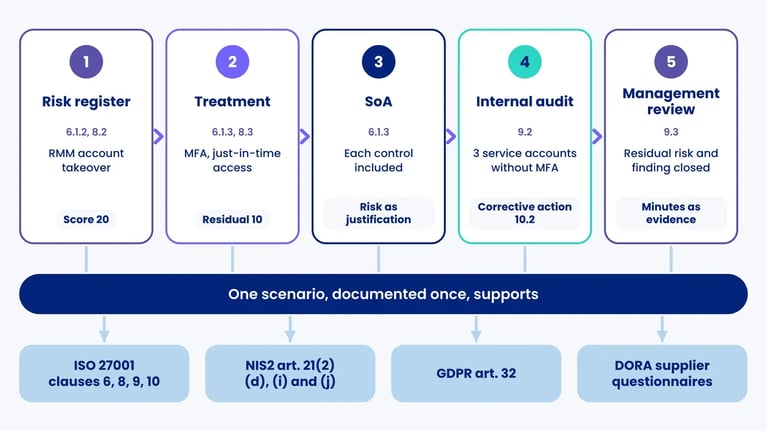
3. Risk assessment (6.1.2, 8.2). One scenario stands out: an attacker takes over an engineer's RMM account and pushes ransomware to customer systems. Likelihood 4, impact 5, so the inherent score is 20.
4. Treatment and SoA (6.1.3, 8.3). The treatment plan adds phishing-resistant MFA for all RMM accounts (A.8.5), just-in-time privileged access (A.8.2), a security review of the RMM vendor (A.5.19-A.5.22) and alerting on unusual mass deployments (A.8.15, A.8.16). Residual risk drops to likelihood 2, impact 5, a score of 10. The COO, as risk owner, signs the acceptance. The SoA records each control as included, with this risk as justification.
5. Objective and measurement (6.2, 9.1). The objective is 100% of privileged RMM accounts on phishing-resistant MFA by the end of the quarter, reported monthly.
6. Internal audit (9.2). The internal auditor samples 25 accounts and finds three service accounts that bypass MFA. That's a nonconformity (10.2). The root cause is that service accounts were never in the MFA rollout plan. The corrective action adds them and updates the onboarding procedure.
7. Management review (9.3). The board sees the residual risk, the audit finding and its closure. The minutes double as evidence under NIS2 art. 20 that management approved and oversees the measures.
One risk scenario, documented once, now supports ISO 27001 clauses 6, 8, 9 and 10, NIS2 art. 21(2)(d), (i) and (j), GDPR art. 32 for the customer data behind those networks, and the answers in the next customer's DORA supplier questionnaire. That reuse is the real business case for an ISMS.
How to build an ISMS in seven steps
There's no single correct sequence, but auditors and experienced implementers tend to follow the order the standard implies. In practice, certification bodies expect evidence that internal audits and a management review have been carried out before the stage 2 audit.
| Step | ISO 27001 clause | Output | Typical owner |
|---|---|---|---|
| 1. Secure management mandate | 5.1, 5.3 | Named ISMS owner, budget, steering forum | CEO or COO |
| 2. Define context and scope | 4.1-4.3 | Scope statement, list of interested parties and their requirements (legal, contractual) | ISMS owner |
| 3. Write the policy and set risk criteria | 5.2, 6.1.2 | Information security policy, risk method and acceptance criteria | ISMS owner with management |
| 4. Assess and treat risks | 6.1.2, 6.1.3, 8.2, 8.3 | Asset inventory, risk register, treatment plan, Statement of Applicability | Risk owners across the business |
| 5. Implement controls and train people | 7.2, 7.3, 8.1, Annex A | Procedures, technical measures, awareness programme | IT, HR, facilities |
| 6. Measure and audit | 9.1, 9.2 | KPIs, internal audit programme and reports | Internal auditor (independent of the work audited) |
| 7. Review and improve | 9.3, 10.1, 10.2 | Management review minutes, corrective actions, updated plan | Top management |
Two practical points. Build the asset inventory from what you already have, such as your GDPR records of processing and your supplier list, rather than starting from zero. And give awareness a real plan with measurable outcomes (A.6.3). Our article on awareness training has ideas that work in practice.
If you decide to certify, the audit runs in two stages, followed by surveillance audits and recertification on a three-year cycle. Our guide to ISO 27001 certification explains the process and what drives the cost. Remember that ISO/IEC 27001:2013 certificates expired or were withdrawn at the end of the transition period on 31 October 2025, under IAF MD 26. A supplier still showing a 2013 certificate has no valid certification.
What an ISMS does not do
An honest answer to "what is an ISMS?" includes its limits. These are the ones we see most often:
- It doesn't make you secure by itself. An ISMS is a way of deciding and checking. A well-documented ISMS with weak controls is still weak.
- A certificate says nothing outside its scope. Always read the scope statement. A certificate covering one data centre tells you little about the SaaS product you're buying.
- It isn't GDPR compliance. Records of processing, lawful basis, DPIAs and data subject rights sit outside ISO 27001. ISO/IEC 27701:2025, now a standalone privacy management system standard, is the closer fit for that.
- It isn't NIS2 compliance either. Registration, the 24/72-hour reporting chain and national specifics must be added.
- It isn't an assurance report. Some customers want an ISAE 3402 or ISAE 3000 report on how controls operated over a period. See our article on ISAE 3402 for the difference.
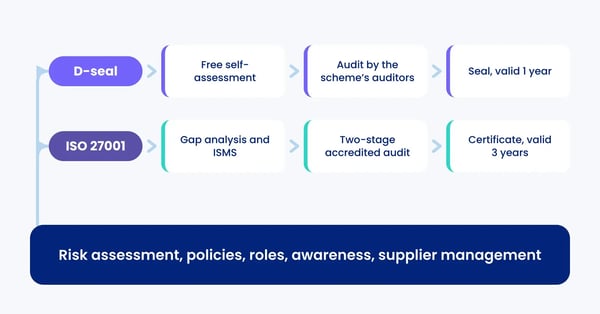
Smaller organisations sometimes start with a lighter label or scheme before ISO 27001. Our comparison of D-seal vs ISO 27001 shows how that choice plays out in practice.
Dates and numbers worth knowing
| Date or figure | What it means | Source |
|---|---|---|
| October 2022 | ISO/IEC 27001:2022 published (Amendment 1 on climate action followed in 2024) | ISO |
| 17 October 2024 | NIS2 transposition deadline | NIS2 art. 41 |
| 17 January 2025 | DORA applies to EU financial entities | DORA art. 64 |
| 31 October 2025 | All ISO/IEC 27001:2013 certificates expired or withdrawn | IAF MD 26 |
| 8 July 2026 | Four member states referred to the Court of Justice over NIS2 transposition | European Commission |
| July 2026 | ISO/IEC 27000:2026 (sixth edition) published | ISO |
| 96,709 | Valid ISO/IEC 27001 certificates worldwide at end of 2024 | ISO Survey 2024 |
How .legal supports your ISMS
Most organisations that ask us "what is an ISMS?" already have parts of one. A policy here, a risk spreadsheet there, supplier reviews in someone's inbox. The work is joining them up so that one risk, one control and one piece of evidence can be reused wherever it's needed.
The information security management module in .legal gives you a structure for ISO 27001:2022 with risk assessments, Annex A controls, the Statement of Applicability and evidence in one place. With Frameworks you can see how the same controls map to NIS2, GDPR and other requirements. Policy Management handles policy versions and acknowledgement, and Compliance Task Management keeps recurring work like internal audits and management reviews on schedule.
The platform won't run your ISMS for you. Risk decisions, control ownership and management's commitment stay with your people. What it removes is the chasing, the duplicate spreadsheets and the scramble for evidence before an audit.
Want to see it with your own scope? Book a demo.

.legal compliance platform
Build Your ISMS with .legal
-
Define and manage security policies
-
Conduct and track risk assessments
-
Monitor security control effectiveness
-
Manage internal audits and reviews
-
Generate compliance documentation