Information security vs cybersecurity: the difference, and why it matters
Information security vs cybersecurity in one line: the first protects all information, including paper, conversations and know-how, the second protects network and information systems from cyber threats. Here are the ISO and EU legal definitions, what the law actually requires, and how to organise the work.

In most organisations, three words are used as if they meant the same thing. The board papers say "cyber". The ISO 27001 documentation says "information security". The IT team just says "security". That rarely matters until someone has to decide who owns a risk, what a security programme should cover, and which authority needs to hear about it when something goes wrong.
This guide settles information security vs cybersecurity using the bodies that actually define the terms: the ISO/IEC 27000 family, the EU Cybersecurity Act and NIS2. It then shows what European law requires, why most reported breaches are not cyber attacks, and how to organise the work.
The short answer: what is the difference between information security and cybersecurity?
Information security is about protecting the confidentiality, integrity and availability of all information, whatever form it takes. That includes data in systems, but also paper files, a conversation in a meeting room and the knowledge a key member of staff carries in their head. Cybersecurity is about protecting network and information systems, their users and other affected people from cyber threats. Its focus is the digital and the connected.
In practice, cybersecurity is mostly a part of information security, but not entirely. Cybersecurity also covers systems where the harm is not primarily to information, such as the control system at a water treatment plant. The most important point in the information security vs cybersecurity question is legal. Even NIS2, a directive about cybersecurity, requires measures that cover the physical environment and human resources security. A security programme that is "cyber only" does not meet it.
Cyber and information security: four terms that get mixed up
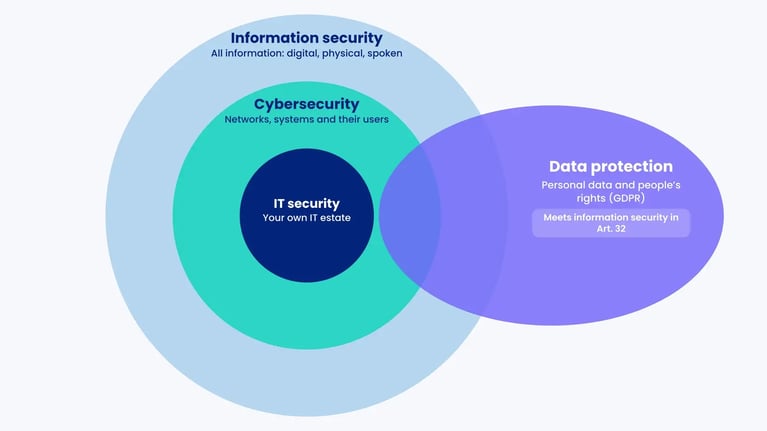
Searches on this topic blend three words, and data protection often sits behind the question too. Place each one before comparing them.
| Term | What it protects | Typical framework |
|---|---|---|
| Information security | All information in the organisation, digital, physical and spoken | ISO/IEC 27001 and an information security management system (ISMS) |
| Cybersecurity | Network and information systems, their users and other affected people | NIS2, the Cybersecurity Act, ISO/IEC 27032, NIST CSF 2.0 |
| IT security | The organisation's own IT estate: hardware, software and operations | Technical controls and operating procedures in the IT function |
| Data protection | Personal data and the rights of the people it relates to | GDPR (and UK GDPR with the Data Protection Act 2018) |
So what about information security vs IT security, or IT security vs cybersecurity? IT security is the most technical and the narrowest of the three. It is about your own systems being patched, correctly configured, monitored and recoverable. Cybersecurity is IT security viewed through the threats that arrive over networks and the internet, and it reaches beyond your own estate to suppliers, users and critical services. Information security is the overall discipline that also takes in people, processes and physical conditions.
Data protection is different again. GDPR protects people, not information as such, but it meets information security in Article 32 on security of processing.
What is information security?
The most widely used definition comes from ISO/IEC 27000, the foundation standard of the ISO 27000 family. The 2018 edition defines information security as the preservation of confidentiality, integrity and availability of information (entry 3.28), and notes that other properties such as authenticity, accountability, non-repudiation and reliability can also be involved. The US National Institute of Standards and Technology uses a very similar definition: the protection of information and information systems from unauthorised access, use, disclosure, disruption, modification or destruction.
Neither definition says the information has to be digital. A printed payroll list, a whiteboard sketch of next year's strategy and an operations manager's knowledge of how to start the backup generator are all information assets. That is why ISO 27001 has controls for clear desk, secure disposal, confidentiality agreements and staff screening.
Three things are worth knowing about the standards in 2026:
- ISO/IEC 27000:2026 was published on 3 July 2026, replacing the 2018 edition. Its title is now "Information security, cybersecurity and privacy protection. Information security management systems. Overview", and ISO describes it as an overview of concepts and relationships rather than a terminology document.
- ISO/IEC 27001:2022 carries the same main title, so the certifiable standard frames all three.
- The transition from the 2013 edition closed on 31 October 2025. Any valid certificate today is issued against the 2022 edition, with 93 Annex A controls in four themes: 37 organisational, 8 people, 14 physical and 34 technological.
Only about a third of the controls are technological. In practice, information security is run through an information security management system (ISMS), in which management sets the scope, policy, risk assessment and ongoing review.
The CIA triad in practice
Confidentiality, integrity and availability are often called the CIA triad. They apply to both information security and cybersecurity, but the examples look different.
| Property | Incident outside the systems | Incident through networks and systems |
|---|---|---|
| Confidentiality | A letter containing health data is posted to the wrong address | An attacker exfiltrates the customer database through a vulnerable web server |
| Integrity | Someone alters a signed paper contract | Bank details on an invoice are changed in a compromised mailbox |
| Availability | The only person who knows a critical procedure leaves the company | Ransomware encrypts the file server and its backups |
What is cybersecurity?
Unlike information security, cybersecurity has a legal definition in the EU. The Cybersecurity Act, Regulation (EU) 2019/881, defines cybersecurity in Article 2(1) as "the activities necessary to protect network and information systems, the users of such systems, and other persons affected by cyber threats". A cyber threat, under Article 2(8), is "any potential circumstance, event or action that could damage, disrupt or otherwise adversely impact network and information systems, the users of such systems and other persons".
The NIS2 Directive (EU) 2022/2555 borrows that definition in Article 6(3). It also defines "security of network and information systems" in Article 6(2) as the ability of those systems to resist events that may compromise the availability, authenticity, integrity or confidentiality of data or of the services they provide.
Two things set this apart from information security. It is digital from start to finish, so paper, conversations and know-how fall outside it. And it protects more than information, namely the users and other people affected. When an attacker takes over a pumping station, the harm is not a leak. It is people losing their water supply.
On the standards side, ISO/IEC TS 27100:2020 describes cybersecurity and how it relates to information security, focusing on risks in cyberspace, an interconnected digital environment that crosses organisational boundaries. ISO/IEC 27032:2023 gives guidelines for internet security. Neither is certifiable, and even commentators in the ISO 27000 community criticise TS 27100 for muddying the waters. Do not expect one definition everyone agrees on.
Information security vs cybersecurity: side by side
A common mistake, which our own earlier version of this article made, is to say information security covers "information only" while cybersecurity covers "data and information". Both protect data and information. The difference lies in the form the information takes and the threats you look for.
| Aspect | Information security | Cybersecurity |
|---|---|---|
| Definition | Preservation of confidentiality, integrity and availability of information (ISO/IEC 27000:2018, 3.28) | Activities protecting network and information systems, users and others affected by cyber threats (Regulation 2019/881, Art. 2(1)) |
| What is protected | Information in any form: digital, paper, speech, know-how | Digital systems, networks and data, plus the people who depend on them |
| Threats | All of them: human error, theft, fire, insiders, suppliers, attacks | Mainly threats via networks and systems: ransomware, phishing, DDoS, exploited vulnerabilities |
| Typical controls | Policies, classification, access management, physical security, awareness, supplier management, continuity | MFA, patching, network segmentation, logging and monitoring, EDR, vulnerability scanning, incident response |
| Standards | ISO/IEC 27001 and 27002, ISO/IEC 27005 | ISO/IEC 27032, ISO/IEC TS 27100, NIST CSF 2.0, CIS Controls |
| Where the term appears in law | Rarely as a legal term. GDPR speaks of security of processing (Art. 32) | Cybersecurity Act, NIS2, Cyber Resilience Act, UK NIS Regulations |
| Success is measured by | Risks within management's appetite, documented and reviewed | Time to detect and contain, patch levels, control coverage |
The table does not describe two competing disciplines. It describes two views of the same job. Information security asks what information we hold, what it is worth and what could go wrong. Cybersecurity asks how someone or something could harm us, or those who rely on us, through our networks and systems.
Where they overlap, and where they don't
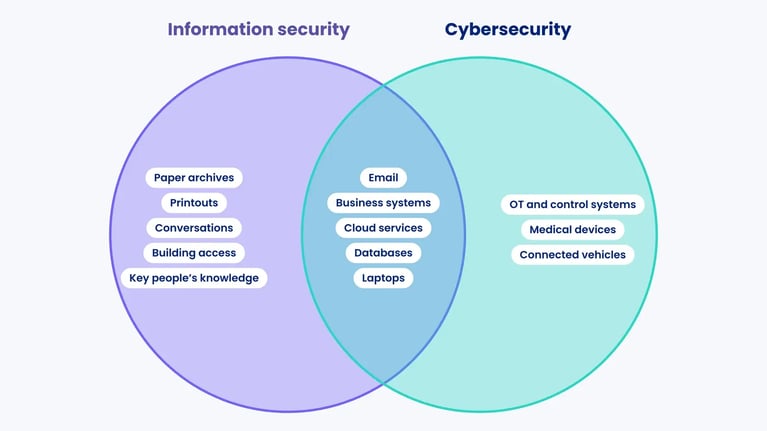
The usual line is that cybersecurity is a subset of information security. That holds for most organisations, but it is more precise to think in three zones.
- Information security only: paper archives, printouts, conversations, building access, key people's knowledge, document disposal.
- Both: email, business applications, cloud services, databases, laptops. A misdirected email is an information security breach through a digital system, with no attacker involved.
- Cybersecurity only: systems where information is not the main thing at stake, such as industrial control systems (OT), medical devices and connected vehicles. The concern is operations, physical safety and essential services.
For a typical organisation with 50 to 500 staff, almost everything sits in the first two zones. For utilities, transport and manufacturing, the third can be the most critical, which is why "cyber" dominates critical infrastructure regulation.
What the law requires: cyber in the title, information security in the text
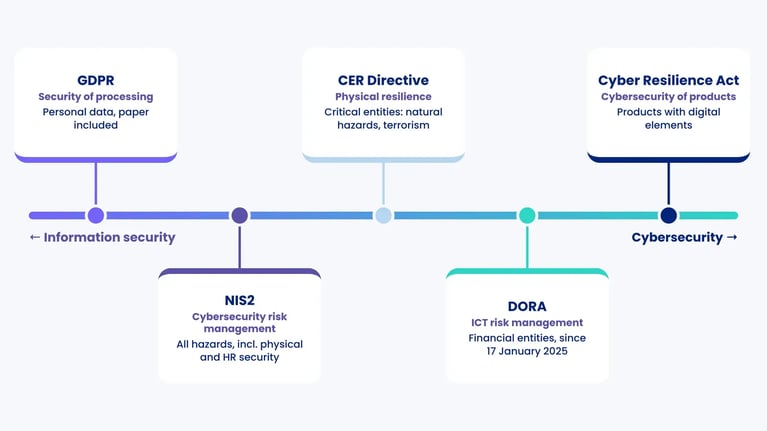
The biggest practical misunderstanding is that a legal duty labelled "cybersecurity" is purely digital. Look at NIS2 itself. Article 21(2) says the cybersecurity risk-management measures "shall be based on an all-hazards approach that aims to protect network and information systems and the physical environment of those systems from incidents". The minimum list includes human resources security, access control policies and asset management (point (i)), supply chain security (point (d)) and business continuity and crisis management (point (c)).
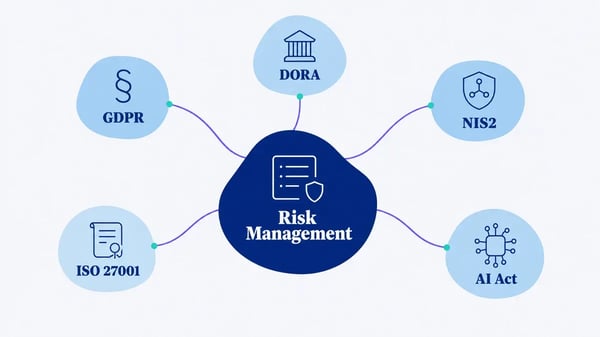
That is classic information security. You cannot comply without looking at people, buildings and suppliers, which is also why ISO 27001 is a strong foundation for NIS2, as our comparison of NIS2 and ISO 27001 sets out.
| Rulebook | Term used | What it actually covers |
|---|---|---|
| GDPR Art. 2(1) and Art. 32 | Security of processing | Personal data processed by automated means and manually in a filing system. Paper is in scope |
| GDPR Art. 33 and 34 | Personal data breach | Notification to the supervisory authority within 72 hours. Data subjects told without undue delay where the risk is high |
| NIS2 Art. 20 and 21 | Cybersecurity risk management | All hazards, including the physical environment, HR security, assets, suppliers and continuity. Management bodies approve and oversee |
| NIS2 Art. 23 | Significant incidents | Early warning within 24 hours, incident notification within 72 hours, final report within one month |
| CER Directive (EU) 2022/2557 | Physical resilience | Critical entities' resilience against natural hazards, terrorism and technical failure |
| Cyber Resilience Act (EU) 2024/2847 | Cybersecurity of products | Manufacturers of products with digital elements. Article 14 reporting has applied since 11 September 2026, the main obligations from 11 December 2027 |
| DORA (EU) 2022/2554 | ICT risk management | Digital operational resilience of financial entities, applicable since 17 January 2025 |
GDPR deserves a closer look. Under Article 2(1), it applies both to automated processing and to manual processing of personal data that forms part of a filing system. Article 32 requires appropriate technical and organisational measures proportionate to the risk. Encryption and pseudonymisation are listed as examples, not as absolute requirements. A GDPR security effort that looks only at cyber threats misses paper and most of the organisational measures.
National implementation and what is changing
NIS2 bites through national law, and transposition has been uneven. The deadline was 17 October 2024, and on 28 November 2024 the European Commission sent letters of formal notice to 23 Member States that had not fully transposed it. Denmark's NIS2 Act, for example, has applied since 1 July 2025, while others are still catching up. Check the national law and competent authority in each country where you operate.
Change is also on the way at EU level. On 20 January 2026 the Commission published a cybersecurity package with a revised Cybersecurity Act and targeted amendments to NIS2. As of September 2026 these are proposals under negotiation, so the rules described above are the ones that apply.
The UK sits outside NIS2. The NIS Regulations 2018 still apply, and the Cyber Security and Resilience (Network and Information Systems) Bill was at report stage in the House of Lords in September 2026, according to the UK Parliament bill tracker. It has not yet received Royal Assent. Read our introduction to NIS2 for the EU side in more detail.
What the numbers show: most breaches are not cyber attacks
The cyber threat is real. ENISA's Threat Landscape 2026, published on 22 September 2026 and covering incidents in 2025, names ransomware as the most impactful incident type in the short term and records more than 48,000 new CVE vulnerabilities published in 2025, a 22% rise on the year before. The 2025 edition identified phishing as the leading intrusion vector in about 60% of observed cases.
Now look at what organisations report to data protection authorities. The UK Information Commissioner's Office publishes data security incident trends. For the fourth quarter of 2025, a Data Protection Network summary (April 2026) puts the split at roughly 77% non-cyber and 23% cyber out of about 3,600 reports, with email sent to the wrong recipient top of the non-cyber list. The Danish Data Protection Agency tells the same story from an EU member state: 9,849 breach notifications in 2025, a record, and in its guidance on the ten typical breaches it states that most notified breaches involve personal data unintentionally shared with the wrong recipients.
| Common breach type | Root cause | Cyber attack? |
|---|---|---|
| Email sent to the wrong recipient, often via autocomplete | Human error | ✗ No |
| Failure to redact personal data before disclosure | Process failure | ✗ No |
| Loss or theft of unencrypted devices or paperwork | Physical loss and missing encryption | ✗ No |
| Overly broad access to shared drives | Access management | ✗ No |
| Unauthorised access through design flaws or coding errors | Secure development | Partly, when the flaw is exploited |
| Phishing leading to account compromise | Social engineering | ✓ Yes |
| Ransomware causing loss and misuse of data | Attack | ✓ Yes |
The list draws on incident categories used by the ICO and the Danish authority, and the right-hand classification is ours. Cyber attacks are the most damaging incidents, and ransomware can halt a business for weeks. But they are not the most frequent. A programme measured only on firewalls, EDR and patch levels misses what goes wrong most often. Our article on security breaches covers how to handle both kinds.
A worked example: three incidents, one programme
Kestrel Freight and Anna Keller are fictional. We invented them for this article, and they are neither customers nor a case study.
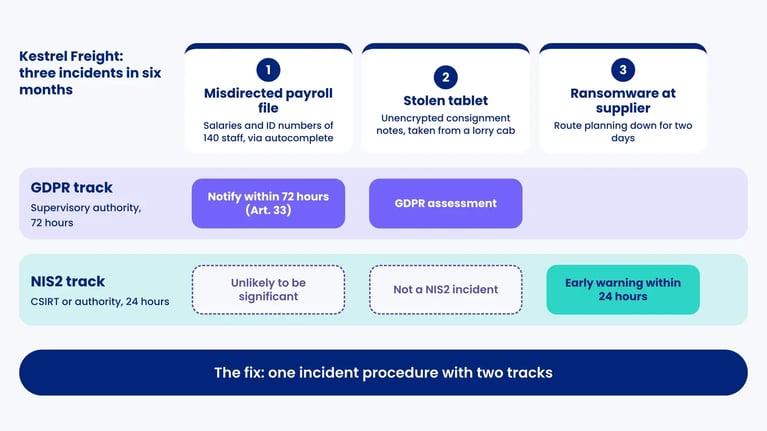
Kestrel Freight is an EU-based road haulier with 140 staff, in scope of national NIS2 law as an important entity. It has a solid cybersecurity programme owned by the head of IT: MFA everywhere, EDR on every endpoint, monthly patching and an external SOC. The risk register holds 38 risks, 33 of them technical. Anna Keller has just joined as head of compliance and information security.
Over six months, three things happen:
- A payroll administrator sends a spreadsheet with salary details and national ID numbers for all 140 employees to the wrong external recipient because of email autocomplete. It is a personal data breach under GDPR Article 4(12) and must be notified to the supervisory authority within 72 hours under Article 33. It is unlikely to be a significant incident under NIS2, because operations are not affected.
- A driver's tablet holding unencrypted consignment notes and customer contact details is stolen from a lorry cab. Physical theft, whose consequences depend on encryption that had not been switched on. A GDPR assessment, not a NIS2 incident.
- Kestrel's route-planning supplier is hit by ransomware, and Kestrel cannot plan routes for two days. This may well be a significant incident under NIS2, triggering an early warning within 24 hours, and it goes straight to the supply chain requirement in Article 21(2)(d).
The cyber programme was relevant only to the third incident, and there the weakness sat with a supplier it did not cover. Anna makes three decisions. She widens the ISMS scope to cover all information, including paper and mobile devices in vehicles. She adds 12 non-technical risks to the register, among them misdirected email, device theft and dependence on key people, so the register now holds 50 risks, 17 of them non-technical. And she creates a single incident procedure with two tracks, a GDPR track to the data protection authority and a NIS2 track to the CSIRT or competent authority, so nobody has to guess in the first few hours.
The head of IT still owns the technical controls. Anna owns the whole, and the management body approves the risk-management measures, as NIS2 Article 20 requires. The lesson of this information security vs cybersecurity example is not that cyber is overrated. It is that a cyber programme without an information security framework around it leaves gaps that GDPR and NIS2 expect to be closed.
How to organise information security and cybersecurity
Roles are where things most often blur when the terms are mixed up. This division of labour works in most organisations with 50 to 1,000 staff:
| Role | Owns | Does not own |
|---|---|---|
| Board and executive team | Risk appetite, approval of measures (NIS2 Art. 20), management review (ISO 27001 clause 9.3) | Day-to-day operation of controls |
| CISO or head of information security | The ISMS, risk assessment, policies, awareness, supplier requirements, reporting to management | Configuring firewalls and endpoints |
| Head of IT security or SOC | Technical controls, monitoring, patching, incident response in the systems | Risks outside the systems, such as paper and physical access |
| Data protection officer (DPO) | Advising on and monitoring GDPR compliance (Art. 39) | The record of processing and breach notification, which are the controller's duties |
In smaller organisations the CISO and head of IT security are often the same person. That is fine, as long as someone is explicitly accountable for what lies outside the systems.
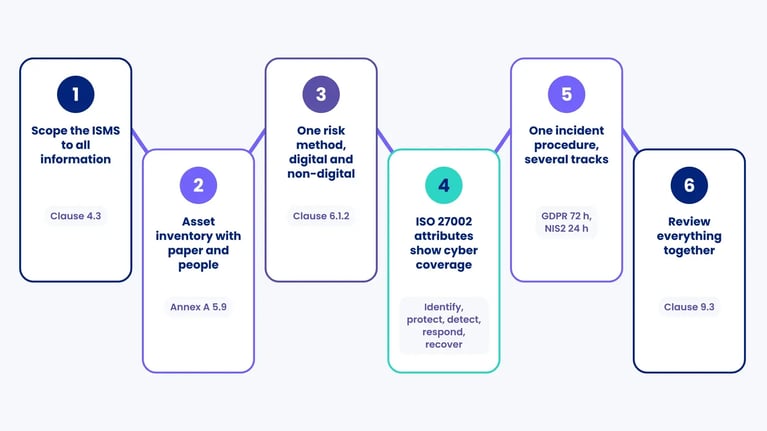
Six steps to one programme
- Scope the ISMS to all information. ISO 27001 clause 4.3 requires you to determine the scope. State that it covers physical information, mobile devices and key people's knowledge, not just IT.
- Build an asset inventory that includes paper and people. Annex A control 5.9 on the inventory of information and other associated assets is not limited to systems.
- Assess digital and non-digital scenarios with one method. Use the same approach under clause 6.1.2 so the risks can be compared. Our guide to information security risk management shows how one method can serve GDPR, NIS2 and ISO 27001.
- Use the ISO 27002 attributes to see your cyber coverage. ISO/IEC 27002:2022 tags each control with the cybersecurity concepts identify, protect, detect, respond and recover. Sorting by them shows whether the technical layer joins up with the rest.
- Create one incident procedure with several tracks. A GDPR track with notification within 72 hours and, if you are in scope, a NIS2 track with an early warning within 24 hours. Rehearse both, for example through awareness training and tabletop exercises.
- Review everything together at management level. The management review under clause 9.3 should cover technical metrics and non-technical risks in one place.
Suppliers with access to your systems or data belong in scope too. See our article on vendor audits.
What the definitions won't solve
Settling information security vs cybersecurity on paper does not solve the problem. Three caveats:
- Usage varies. "Cyber" can mean anything from firewalls to national resilience. Write your own definitions into your security policy.
- The standards are moving. ISO/IEC 27000:2026 has only just been published and has changed how terms are maintained across the family. Check the exact wording if you quote definitions in your documentation.
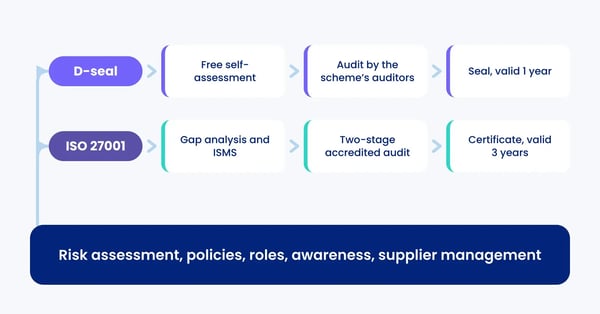
- Certification is not proof of legal compliance. An ISO 27001 certificate shows you run a working management system. It does not make you compliant with GDPR or NIS2 by itself. Read more about ISO 27001 certification and, if you sell into Denmark, our comparison of the D-seal and ISO 27001.
How .legal supports information security and cybersecurity
The practical challenge is rarely understanding the difference. It is keeping the misdirected email, the stolen tablet and the supplier's ransomware attack in the same risk register and management report.
In the .legal platform's information security management module, you record your assets, including non-digital ones, and link them to risks and controls. Risk management uses the same method for digital and physical scenarios. In Frameworks, you map one control to both ISO 27001 and NIS2, so you do not document the same thing twice. Suppliers are handled in Vendor Management, your security policies in Policy Management, and recurring tasks such as awareness, access reviews and the management review go into compliance task management.
The platform does not replace your technical security tools or make you compliant on its own. It gives you the structure to document, assign and follow up the work. To see it in practice, book a demo.

.legal compliance platform
Manage Information Security with .legal
-
Manage information security policies and controls
-
Track cybersecurity measures and incidents
-
Conduct comprehensive risk assessments
-
Monitor compliance across security frameworks
-
Generate security audit reports