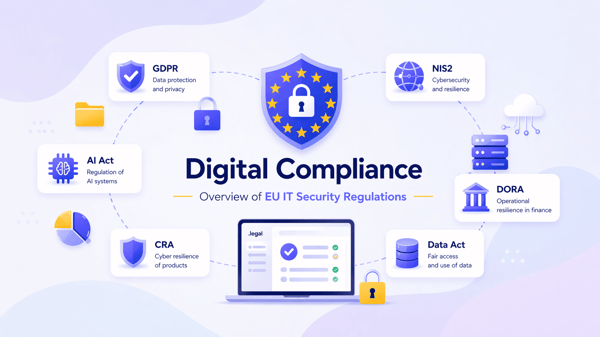
Digital Compliance
In recent years, several new EU regulations have been introduced that impose requirements on organisations' IT security. Get a comprehensive overview of GDPR, NIS2, the AI Act, CRA, Data Act and DORA.
Read more
In recent years, several new EU regulations have been introduced that impose requirements on organisations' IT security. Get a comprehensive overview of GDPR, NIS2, the AI Act, CRA, Data Act and DORA.
Read more
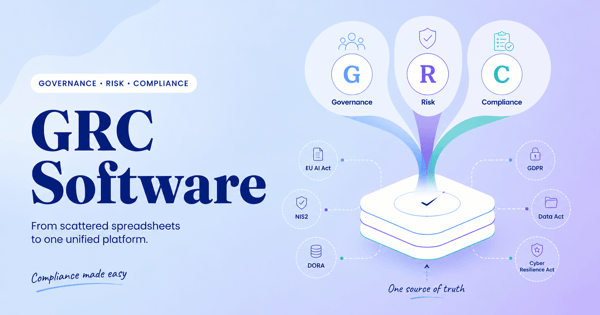
GRC software unifies governance, risk and compliance in a single platform, so one task can satisfy GDPR, NIS2, ISO 27001 and the AI Act at once. Here is what GRC software does, why it beats spreadsheets, and how to choose the right one.
Read more
It is a common practice for organisations to use software to support their GDPR compliance.
Read More
Maybe you don't need GDPR compliance for your business? This article will explore, whether it's a necessary investment for your organisation.
Read More
Have you considered which features to look for when comparing GDPR compliance software?
Read More
It’s not all about features and pricing. Once you commit to a particular compliance software provider, switching later can be challenging.
Read More
List prices for GRC software can't be compared directly. Ask every vendor the same seven questions, put the answers in one sheet and work out what you'll actually pay over three years.
Read more
Do you work with GDPR Compliance and handle your documentation in Excel? Is it becoming difficult to maintain your overview and keep documentation updated?
Read More
The big dilemma. We all have to comply with GDPR. There's not much to discuss here. But there are many paths to compliance, and no two organisations are the same when it comes to privacy. Different personal data is collected in different ways and for different purposes.
Read More
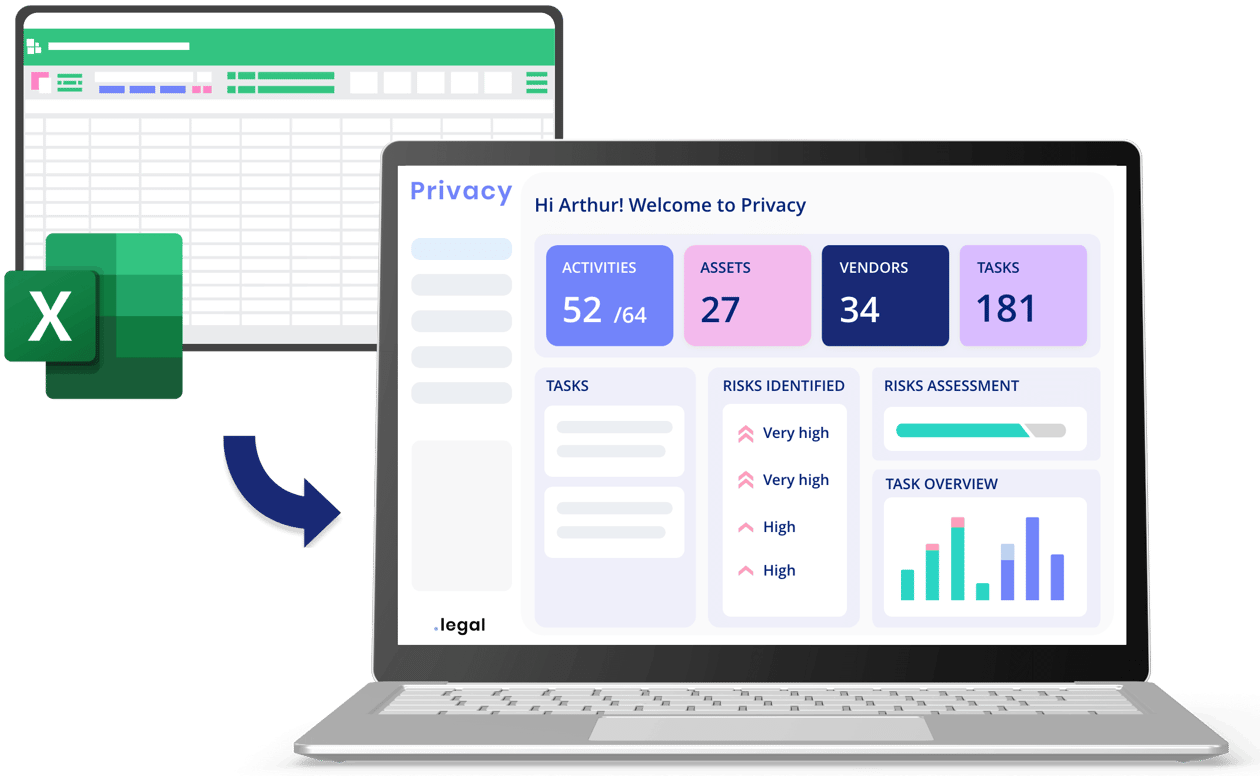
If you're looking for a new GDPR software provider, this article is for you. In this article, you will learn how to migrate from your current provider to the .legal platform.
Read More
GRC stands for Governance, Risk and Compliance - three interconnected elements that form the foundation of effective business management. When you understand what GRC means, you can strengthen your organisation's resilience and ensure sustainable growth.
Read More
Most GRC implementations stall for organisational reasons, not software. This guide shows how clear ownership, simpler processes and documentation you can maintain keep yours moving, with RACI, roadmap and KPIs mapped to NIS2, DORA, GDPR and ISO 27001.
Read more
Digital sovereignty concerns control over your digital future—data, software, and infrastructure. Discover how GDPR, NIS2, DORA, and the Data Governance Act strengthen digital sovereignty whilst ensuring compliance.
Read More
What is a security breach? Understand the difference between GDPR personal data breaches and NIS2 incidents.
Read more
Which GRC platform should you look at? Start with what's driving the purchase, match it to the right type of platform, and test every vendor with the same ten demo scenarios. Here's how to build a shortlist in one week.
Read more