
FRAMEWORK
GDPR framework for controllers and processors
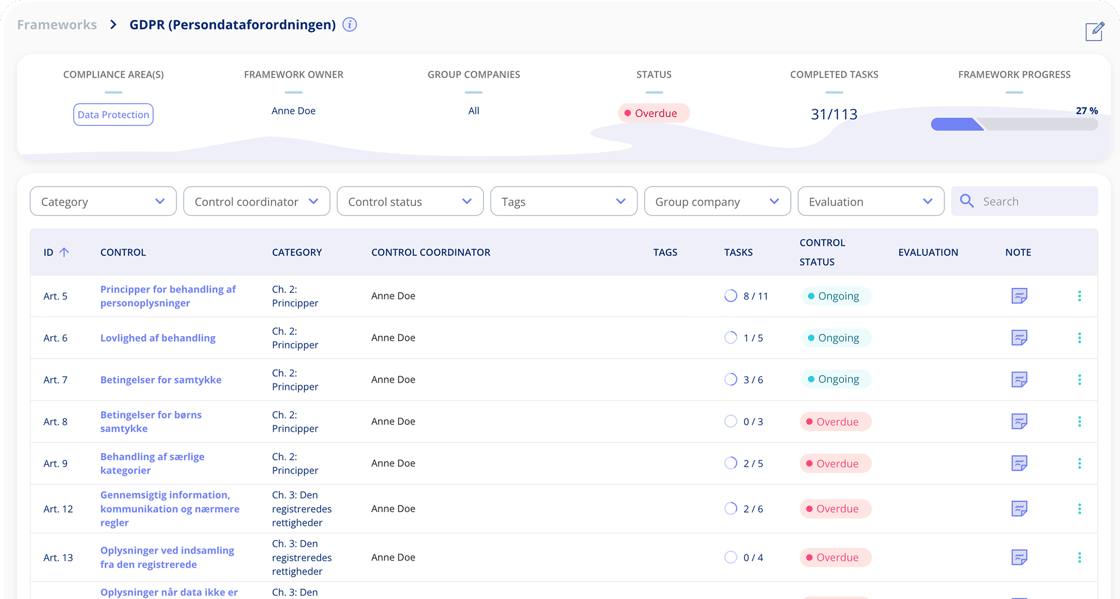
The GDPR framework comes in two variants: one for data controllers with 33 controls and one for data processors with 26 controls. You choose the variant that fits your role.

GDPR FRAMEWORK
GDPR controls in two variants
The GDPR framework uses the same engine as the other frameworks in .legal: controls with tasks from the shared task catalogue, a frequency, an owner and progress. It is part of the Data Protection module, which is described under GDPR compliance software. If you first want to know what the regulation demands, start with the GDPR requirements.
Choose your variant:
-
When you are a controller Use the controller variant with 33 controls. They cover the principles (Articles 5–9), data subject rights (Articles 12–22), controller and processor (Articles 24–39) and transfers to third countries (Chapter V).
-
When you are a processor If you process personal data on behalf of a controller, your obligations are different: you process on documented instructions under a data processing agreement (Article 28), keep a record under Article 30(2) and secure the processing (Article 32). Use the processor variant with 26 controls instead of adapting the controller variant.
GDPR FRAMEWORK
Build upon your existing compliance work
The GDPR Framework integrates seamlessly with your existing compliance programmes. Security controls often satisfy both GDPR and information security requirements, and documentation can be reused across frameworks.
Examples of overlapping frameworks:
-
ISO 27001 Information security management directly supports GDPR's requirements for technical and organisational measures to protect personal data.
-
NIS2 Incident handling and security measures overlap with GDPR's breach notification obligations and security requirements.
-
AI Act Transparency and documentation requirements share common ground with GDPR's principles around lawful processing and data subject rights.
-
ePrivacy Cookie consent and communication privacy build upon GDPR's legal basis requirements and complement your data protection efforts.


-
Lægeforeningen Michael Berner (Lawyer).legal has been the right choice for us. .legal are professional and welcoming with skilled employees.
-
Min By Media Tinna Schultz (HR manager)It just works! It is so easy and user-friendly, and the overview of processing activities is brilliant.
-
Bech-Bruun Mikkel Friis Rossa (Partner).legal's team has consistently demonstrated a commitment to innovation while being responsive to the needs of our mutual clients.
-
DMJX Kaspar Rochholz (GDPR coordinator).legal has really understood what it means to create a user-friendly and efficient solution. Privacy is an attractive product compared to price and functionality.
-
Axel Kaufmann ApS Julie Lundkvist Andreasen (Lawyer and Head of Customer Service).legal continuously update the platform to ensure their customers always remain compliant. In our view, any other choice would be a downgrade.
-
Molecule Consultancy Nanna Rodian Christensen (HR & Operational Manager)Firstly, it means that not all the work is in one place (me), and secondly, that the understanding of GDPR is implemented throughout the organisation.
-
Fenerum Rasmus Boutrup (Financial Controller)With .legal, we've gained a simpler and more manageable solution that better suits our needs
-
Novicell Julie Oxenvad (Legal Consultant)We are satisfied with the switch to .legal – it has strengthened our compliance work, made processes easier to manage and more transparent, and improved cross-team collaboration




























