Skip to content

Risk

Read articles about Risk Management.
Information Security Risk Management: One Method, Many Obligations
Risk › Risk Assessment

Information Security Risk Management: One Method, Many Obligations

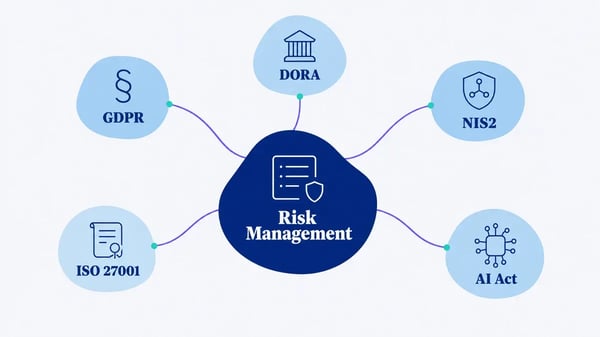
GDPR, NIS2, DORA, the AI Act and ISO 27001 all demand documented risk work. Most organisations run them as separate projects. This guide shows how one method covers them all, with the standards, the article numbers and the practical steps.

Read more arrow
Data Privacy Risk Management - Best Practices and Frameworks
Risk › Risk Assessment

Data Privacy Risk Management - Best Practices and Frameworks

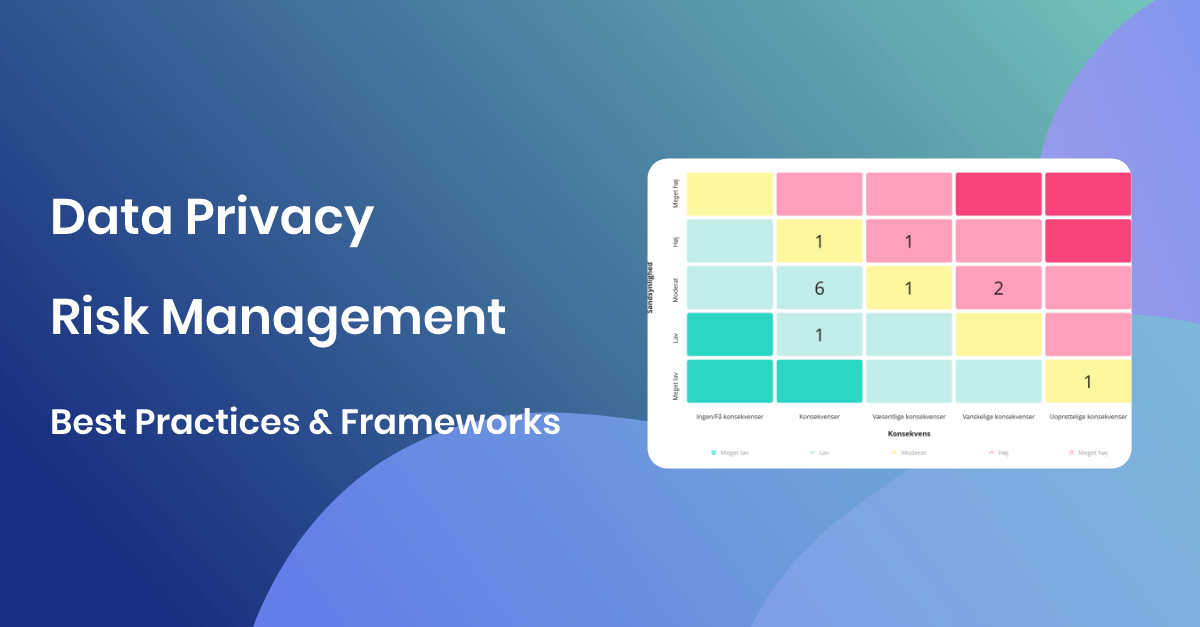
Master GDPR risk assessment with proven frameworks, step-by-step guidance, and real-world examples to protect personal data and ensure compliance.

Read More arrow
What is a risk assessment matrix
Risk › Risk Assessment

What is a risk assessment matrix

Learn how to apply a risk assessment matrix in this article.

Read More arrow
ISO 27005: How to Identify and Assess Information Security Risk
Risk › Risk Assessment

ISO 27005: How to Identify and Assess Information Security Risk

Learn about ISRM in this article and how to apply it in your Information Security Governance.

Read More arrow
+400 companies use .legal
Region Sjælland
Aarhus Universitet
aj_vaccines_logo
Realdania
Right People
IO Gates
PLO
Finans Danmark
geia-food
Evida
Klasselotteriet
NRGI1
BLUE WATER SHIPPING
Karnov
Ingvard Christensen
VP Securities
AH Industries
Lægeforeningen
InMobile
AK Nygart
DEIF
DMJX
Axel logo
qUINT Logo
KAUFMANN (1)
SMILfonden-logo
kurhotel_skodsborg
nemlig.com
Molecule Consultancy
Novicell