Skip to content

Catch the risk when somebody notices it

One public link with no login, so any colleague can report what they spotted from a phone in half a minute. It lands in an inbox with an owner, where a person decides whether it becomes a risk scenario.

Unlimited users  •  Free onboarding and support  •  No commitment
Illustration of a colleague holding up a phone with a short form on it, a thin line carrying the report into an open inbox tray of cards, and two more colleagues beside a blank sign further back
+400 companies use .legal
Region Sjælland
Aarhus Universitet
aj_vaccines_logo
Realdania
Right People
IO Gates
PLO
Finans Danmark
geia-food
Evida
Klasselotteriet
NRGI1
BLUE WATER SHIPPING
Karnov
Ingvard Christensen
VP Securities
AH Industries
Lægeforeningen
InMobile
AK Nygart
DEIF
DMJX
Axel logo
qUINT Logo
KAUFMANN (1)
SMILfonden-logo
kurhotel_skodsborg
nemlig.com
Molecule Consultancy
Novicell
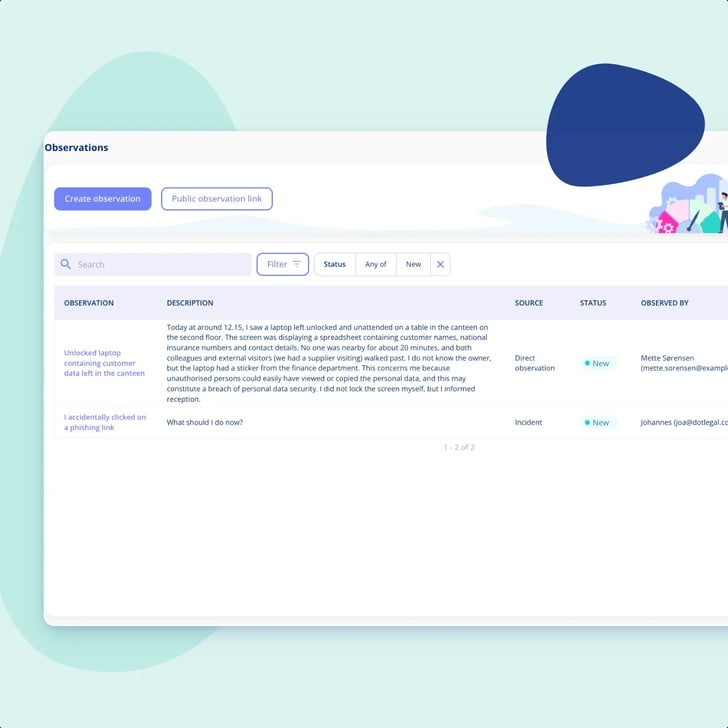
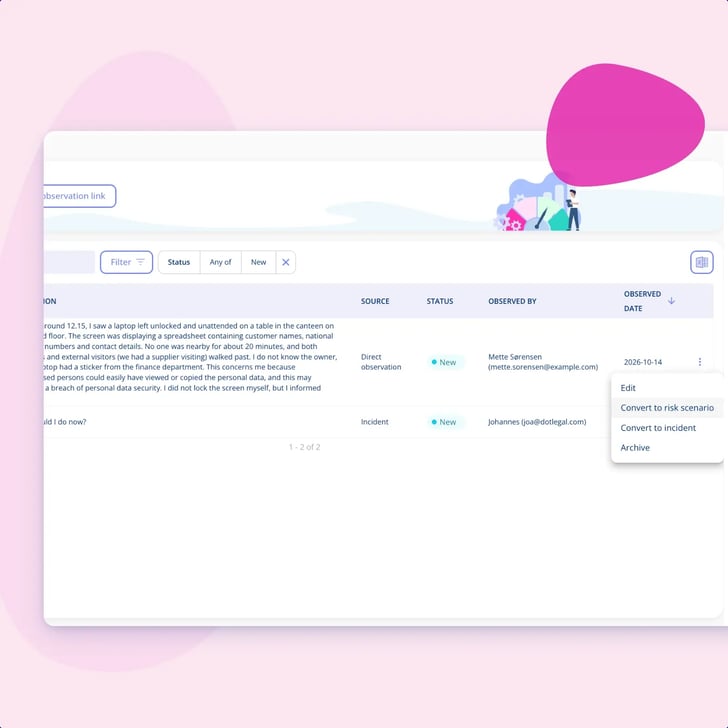
The Observations inbox in .legal with two new observations, one describing an unlocked laptop left in the canteen, each with its source, status and the name of the person who reported it

Risk observations

Meridian's risk register now starts with people who never log in

A technician on a service round notices that only one of three pumps in a technical room is still running. She has no login to Meridian's compliance platform and no reason to want one, so she opens a link on her phone, writes down what she saw and gets on with the round. Meridian Nordic is an energy and utilities group, 850 people across Denmark, Sweden and Germany, with NIS2 to answer to and a certified information security management system to keep, and Anders Krogh is the CISO who used to be the only route into its risk register. Now the register starts with her, and the review starts with him.

  • One public link with no login, so 850 colleagues can report something without a seat in the platform.
  • Every observation arrives with a name and an email on it, so the review can begin with a question rather than a guess.
  • The link does not expire, which is why it can sit on the intranet, in onboarding material and on a printed sign at a site.
  • Closing an observation is a valid outcome on the record, so the register fills up with risks instead of noise.

  • Half a minute, no login

    A colleague opens a public link on their phone, writes what they saw and is done. No account, nothing to install.

  • One link you can print

    The link does not expire, so the same one can sit on the intranet, in onboarding material and on a sign in the building.

  • A name on every report

    The reporter gives name and email, so whoever reviews it can go back and ask what they actually saw.

  • Closing it counts

    Not everything needs to become a risk. A person reviews each observation, and closing one is a valid outcome on the record.

Illustration of a figure with an empty speech bubble beside three machine cylinders, only one of them running, and a line that stops in mid-air short of a closed panel, with unused note cards on the floor

Risk observations

The observation happens on a Tuesday, not in the risk hour

Most of what an organisation needs to know about its own risk is noticed by somebody who has no reason to open a compliance platform. It gets mentioned at a handover, and then the day moves on.

  • The people standing closest to the equipment are the people least likely to have a login.
  • By the time the risk work comes round again, the detail that mattered has gone soft.
  • Nobody files a form that costs them an account, a password and a guess about which module it belongs in.
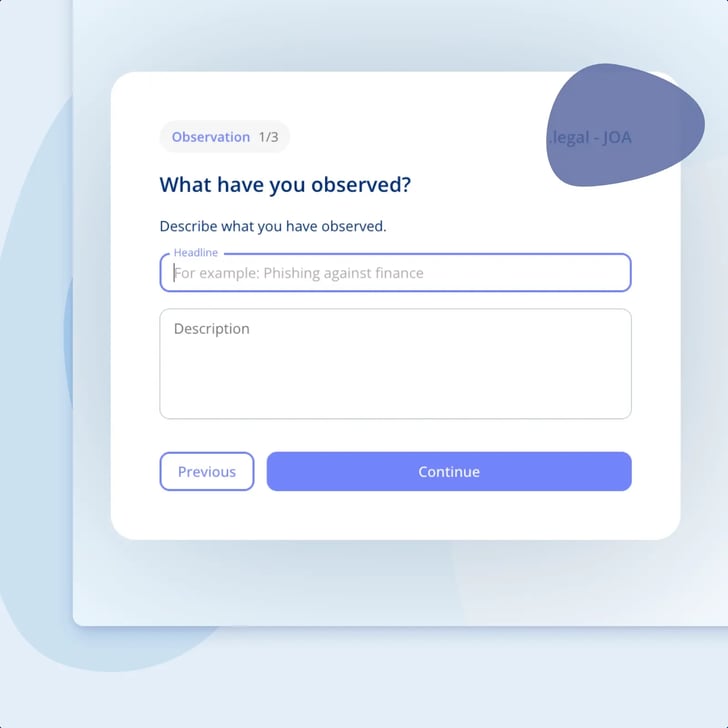
The first step of the public observation form, asking what you have observed, with a headline and a description field and Previous and Continue buttons

Risk observations

One link, no login, half a minute on a phone

The link is public, there is no login in front of it, and the form is deliberately short. This is also the second place in the platform where somebody without a seat can do useful work.

  • Open the link on a phone, write what you saw, send it. No account, and nothing to install.
  • You do not have to know which risk area it belongs to, and consequence and probability can be left empty.
  • The other no-login route points the other way: an assessment you sent out about a named activity. An observation is the opposite, nobody asked for it.
Illustration of a blank sign on a post with lines out to the same link in three places: a card pinned to a wall, a leaflet and a phone held by a colleague

Risk observations

A link that does not expire is a link you can print

The link is permanent. That sounds like a small detail until you have tried to keep a temporary one alive across three countries and a shift pattern.

  • One link goes on the intranet, into the onboarding material, and onto a sign in the building where the equipment is.
  • Nobody has to reissue it, and nobody has to explain why the old link stopped working.
  • Because there is no login in front of the form, the review in the inbox is what decides what enters the register.
Illustration of a record card with an identity badge fixed to its corner, a plainly visible reporter on one side and a reviewer at a desk on the other, joined by a two-way line

Risk observations

Every observation has a name on it

The person reporting states their name and email. That has an obvious upside, and one thing we would rather be blunt about than leave for you to discover.

  • The upside: whoever reviews it can go straight back and ask what they actually saw.
  • The blunt part: observations are attributed, never anonymous.
  • So this is not a whistleblower channel, and it should not be introduced to your colleagues as one.
An observation's menu open in the inbox, with Convert to risk scenario highlighted alongside Edit, Convert to incident and Archive

Risk observations

A person reads it, then converts it or closes it

Everything reported lands in an inbox with an owner. From there it goes one of two ways, and both of them are a result.

  • Convert it into a risk scenario in one step, and the person responsible for the area is notified automatically.
  • From there it joins the normal assessment flow: consequence, probability and a justification on both.
  • Or close it. Not everything needs to become a risk, and reviewing openly is what keeps people reporting.
Illustration of a colleague placing a card by hand into an open tray of cards, while an empty bowl stands apart, unconnected and unused

Risk observations

It receives what a person files, and nothing more

Three things that are easy to assume in our favour, so we will say them ourselves.

  • We do not subscribe to external security advisories on your behalf. Somebody who reads one and thinks it matters files it through the same link.
  • The platform records what a person reports. It does not scan your services and it does not raise anything on its own, so it is not a SIEM.
  • We do not judge relevance for you either. Somebody in your organisation reads each observation and makes that call.
.legal in practice

Features for risk observations

Observations (Enterprise)

Report what you noticed from wherever you noticed it, through a public link with no login and a form built for a phone. Nothing to install, and no category to get right before you can send it.

One permanent link

One shareable link that does not expire, so you put it up once instead of replacing it later. Print it where the work happens, not where the risk work happens.

Attributed, not anonymous

Name and email come with every observation, so a review can start with a question to the person who filed it. It is not an anonymous hotline, and you should know that before the link goes up.

An inbox with an owner

Everything reported lands in one place, where a person reviews it rather than a rule sorting it. Nothing reaches the risk register before somebody has read it.

One step to a risk scenario

Convert a relevant observation into a risk scenario in one step, with the person responsible for the area notified automatically. From there it follows the normal assessment flow.

Close it, and say so

Not every observation belongs in the register. Closing one is a valid outcome that stays on the record, and it is what keeps the register worth reading.

.legal compliance platform

Catch risk from your colleagues with...

Do you need the people who notice a risk to be able to report it? We recommend the following modules for that task.

Information Security Management

Run your information security management and meet NIS2, ISO 27001 and more in one place. The risk work an observation feeds into sits alongside it, not inside it.

Explore Information Security Management

Our Customers

+400

companies

+11.000

users

+79.000

contracts

+14.000

processing activities

Mikkel Friis

Bech-Bruun

Mikkel Friis Rossa (Partner)

.legal's team has consistently demonstrated a commitment to innovation while being responsive to the needs of our mutual clients.

Rasmus-boutrup-fenerum

Fenerum

Rasmus Boutrup (Financial Controller)

Case Study
With .legal, we've gained a simpler and more manageable solution that better suits our needs
Michael Berner 1

Lægeforeningen

Michael Berner (Lawyer)

.legal has been the right choice for us. .legal are professional and welcoming with skilled employees.
Nanna Rodian Christensen

Molecule Consultancy

Nanna Rodian Christensen (HR & Operational Manager)

Case Study
Firstly, it means that not all the work is in one place (me), and secondly, that the understanding of GDPR is implemented throughout the organisation.
ulrikdueholmbeckmann

Plum Safety

Ulrik Dueholm Beckmann (QC, CM og ESG Lead)

Case Study
From .legal, we experience an incredibly high degree of flexibility and willingness to adapt features to our local needs.
julie-oxenvad-novicell

Novicell

Julie Oxenvad (Legal Consultant)

Case Study
We are satisfied with the switch to .legal – it has strengthened our compliance work, made processes easier to manage and more transparent, and improved cross-team collaboration
Tinna Schultz

Min By Media

Tinna Schultz (HR Manager)

Case Study
It just works! It is so easy and user-friendly, and the overview of processing activities is brilliant.
ansat_Kaspar_Rochholz_005

DMJX

Kaspar Rochholz (GDPR Coordinator)

Case Study
.legal has really understood what it means to create a user-friendly and efficient solution. Privacy is an attractive product compared to price and functionality.
Profile-picture1

Axel Kaufmann ApS

Julie Lundkvist Andreasen (Lawyer and Head of Costumer Service)

Case Study
.legal continuously update the platform to ensure their customers always remain compliant. In our view, any other choice would be a downgrade.

NRGi

Mette Mühlendorph (Compliance Specialist)

Case Study
The implementation of .legal has made a difference in the way we handle compliance. The system has created structure and overview, which has had concrete benefits.
Use cases

Find the job you need done

Every use case is a real piece of compliance work, told the way it actually runs in the platform. Filter by who you are, what you work with, and which frameworks you answer to.

Book demo

22 use cases

Compliance & GRC lead

Build one risk register for the whole organisation

One register across GDPR, NIS2, AI and information security, where each risk area keeps its own matrix, scale and appetite. Delivered by the Enterprise Risk Management add-on.
See the risk register
Compliance & GRC lead

Run awareness training that reaches every colleague

Send out training and policies, chase the stragglers automatically, and prove every colleague completed it. You bring the material, we run the rails.
See awareness training
Compliance & GRC lead

Manage compliance across a group of companies

Run every company in the group from one platform, document once at group level, and still report entity by entity. Delivered by the Group Companies add-on.
See group compliance
Legal counsel

Run due diligence on your vendors

Classify a vendor on your own criteria, get the answers and documents you need with no login for them, and move the approved ones straight into contracts.
See vendor due diligence
Compliance & GRC lead

Multi-framework compliance: do the work once

Do a control once and it counts across every framework it maps to, with a simulated score on the ones you haven't started yet.
See multi-framework compliance
CISO & IT security

Get NIS2-ready without starting from scratch

Build on the ISO 27001 work you've already done, switch NIS2 on, and let a simulated score show how far ahead you already are.
See NIS2 readiness
DPO

From twelve spreadsheets to one record of processing

Your GDPR documentation already exists, it just lives in spreadsheets. Export what you have and we structure it in .legal for you, typically inside two weeks.
See the move off spreadsheets
Executive & board

Give the board a risk picture it can act on

One management report across every risk area: entities assessed, risks above appetite, exposure now and once the open plans are done. Export it with your own comment on it.
See board risk reporting

Frequently Asked Questions about risk observations

Do our colleagues need a user account to report an observation?

No. Observations come in through a public link with no login, and the form is deliberately short and built for a phone. That matters most for the people furthest from a desk, because they are usually the ones who notice something first and the least likely to have a seat in the platform. Nothing has to be installed, and there is no password to keep track of.

Run awareness training that reaches every colleague

Is an observation anonymous?

No, and that is worth being clear about before you put the link on a sign. The person reporting states their name and email, so every observation is attributed. The upside is real: whoever reviews it can go back to the person and ask what they actually saw, which is usually the difference between a usable observation and a guess. The consequence is just as real, so we will say it plainly. This is not an anonymous channel and it is not a whistleblower scheme, and it should not be introduced to your colleagues as either.

Does the link expire, and can we switch one off?

The link is permanent, so it does not expire. That is the point of it: one link can sit on the intranet, in onboarding material and on a printed sign for years without anybody reissuing it. Whether a link can be switched off again is not something we have documented, so put that question to us on a demo instead of reading an answer into this page. What we can say is where the control sits today. Because there is no login in front of the form, the review step in the inbox is what decides what enters your risk register, and a person does that review.

Does .legal subscribe to external security advisories for us?

Not at the moment, and it is better you hear that here than assume it. There is no external subscription and no feed bringing advisories into the platform. What works instead is the same link: somebody in your organisation reads an advisory, decides it is relevant to you, and files it as an observation like any other. It then goes through the same review as everything else, which also means somebody has judged that it applies to your estate rather than to the sector in general.

What happens to an observation after somebody files it?

It lands in an inbox with an owner, and a person reviews it. From there it goes one of two ways. If it is worth acting on, it converts into a risk scenario in one step and the person responsible for the relevant area is notified automatically, after which it follows the normal assessment flow with consequence, probability and a justification on both. If it is not, you close it. Both are outcomes, and both stay on the record.

Does the person reporting have to know which risk area it belongs to?

No, and that is deliberate. An observation can be filed independently of risk area, and consequence and probability can be left empty. A technician who notices something on a service round should not have to learn your risk model first, and asking them to would cost you the observation. Placing it in the right area and putting numbers on it is the job of the person reviewing the inbox, and they have the whole model in front of them.

What a risk assessment involves

Can we control who acts on an observation?

Not in a way we would build a process on today, and it is better you hear it here than find out later. Access decides what somebody can reach in the platform, but the step from an observation to a risk scenario is not gated by role. Where that line should sit is a question about your organisation rather than about the product, so bring it to a demo.

Do all our colleagues and suppliers need seats in the platform?

No, and the two routes are cut on direction rather than on mechanics. Observations point inwards and nobody asked for them: a public link with no login that anybody in your organisation can use to report what they noticed, landing in a risk inbox. The audit engine points outwards: a questionnaire you have sent about a named activity or supplier, answered by the person you sent it to, who does not become a user either. They are two different features, so ask about them separately, but between them they cover most of the people who have to do something in your compliance work without a seat.

What due diligence on a supplier involves

Is this included, or is it something we buy?

It is a purchase. Observations belong to Enterprise Risk Management, and both arrived in August 2026. Enterprise Risk Management is part of the Enterprise plan, and what it costs for your setup is agreed with you rather than a line on a page, so bring it to a demo.

Does the platform find these risks by itself?

No, and that boundary is worth drawing hard. The platform receives what a person files. It does not scan your services, it does not watch anything, and it does not raise something on its own, so it is not a SIEM and should not be bought as one. What it gives you is somewhere for a human observation to land, a review step, and a documented route from a report to an assessed risk.

Still unsure?

Ask Johannes directly, he runs most demos personally

Book him here
+400 companies use .legal
Region Sjælland
Aarhus Universitet
aj_vaccines_logo
Realdania
Right People
IO Gates
PLO
Finans Danmark
geia-food
Evida
Klasselotteriet
NRGI1
BLUE WATER SHIPPING
Karnov
Ingvard Christensen
VP Securities
AH Industries
Lægeforeningen
InMobile
AK Nygart
DEIF
DMJX
Axel logo
qUINT Logo
KAUFMANN (1)
SMILfonden-logo
kurhotel_skodsborg
nemlig.com
Molecule Consultancy
Novicell