NIS2 controls, 1:1
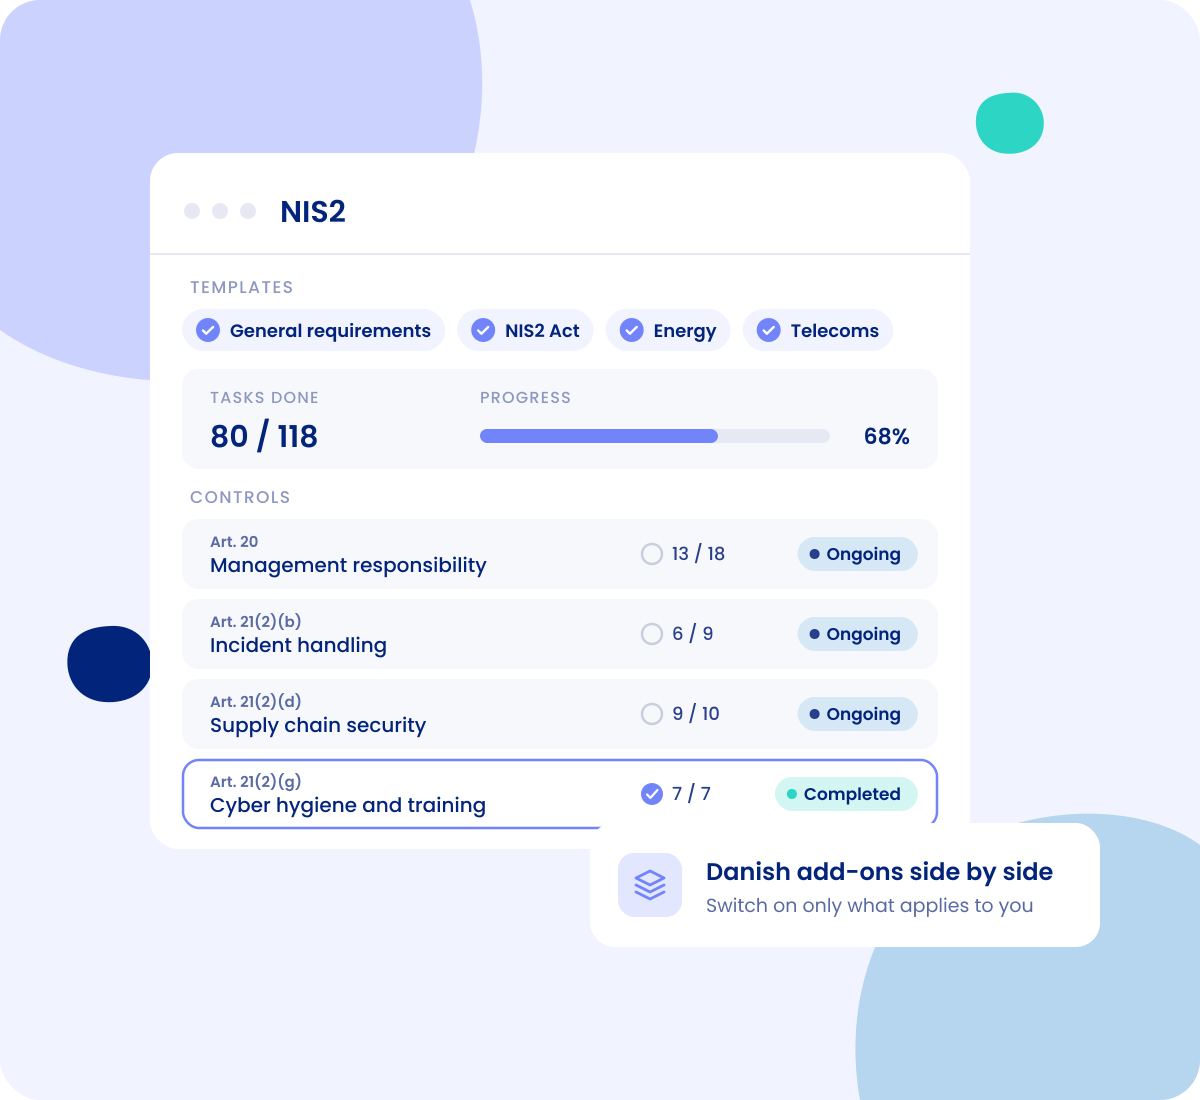
The NIS2 controls match the source 1:1, with tasks underneath that say what has to be documented.
Modules
.legal AI
All AI features →Integrations
See all integrations →Platform & features
Understand the rules
See it in action
All customer stories →Plan your switch
Stay up to date
NIS2 with a partner
"We're covered by NIS2, but we don't have a security department. Who is going to do the work?" Split it task by task. You keep the decisions, a partner advises and implements, and .legal holds the structure, the templates and the follow-up.
NIS2 with a partner
Most organisations that fall under NIS2 without a security team know the requirements are there. What they lack is somebody to own them. The security measures end up spread across people who already have a full-time job.
You decide
The risk appetite, the policies and the incident report to the authority. The decisions stay with you, and management approves the measures.
A partner advises
An implementation partner facilitates the risk assessment, writes or adapts the policies and prepares the material for management.
The platform keeps track
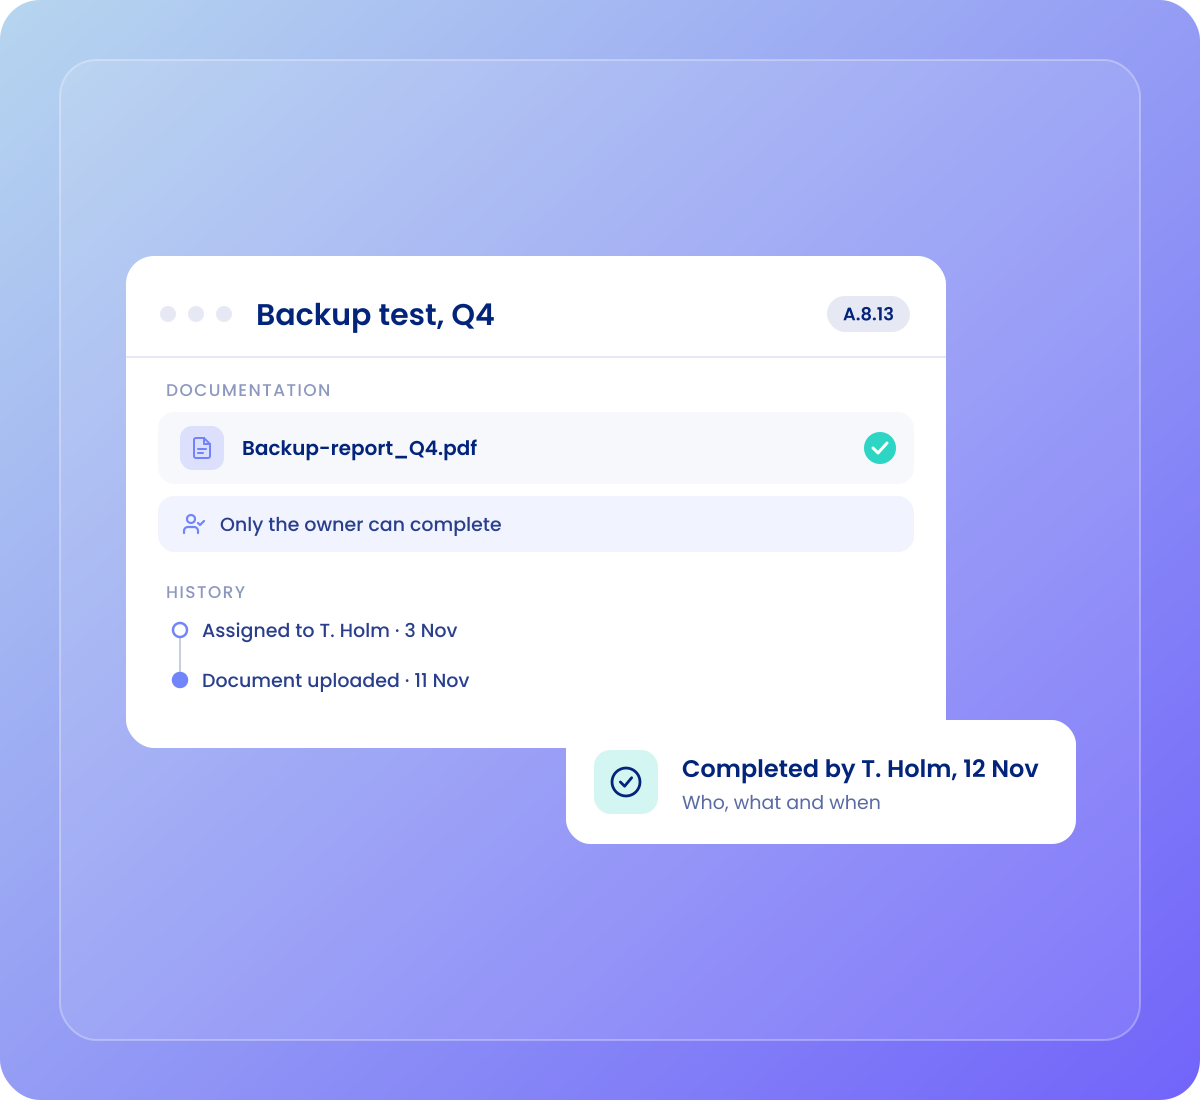
.legal holds the NIS2 controls, the templates and the tasks with owners and due dates, so the work is documented as it is done.
Help to get started
Onboarding and support are included, and .legal helps you bring existing data in from Excel.
Six tasks take most of the time under NIS2. Read each row across: what you do yourselves, what the platform does and what a partner does.
| Task | You | The platform | A partner |
|---|---|---|---|
| Risk assessment | Decide the risk appetite and accept the residual risks. | NIS2 controls that match the source 1:1, risk scenarios from the catalogue in the risk assessment module, and tasks with owners and due dates. | Facilitates the assessment and proposes measures. |
| Policies | Approve the policies and send them out. | Stores them, links them to controls and collects sign-off with Policy Management. See how sign-off works. | Writes or adapts the policies. |
| Suppliers | Own the supplier relationship. | Registers the suppliers and sends audits and due diligence to one supplier or to many at once. See supplier audits in practice. | Helps set the criteria for classification and the questions. |
| Incidents | Report to the authority, and keep track of the reporting deadlines yourselves. | The NIS2 incident template, when the incident happened and when it was reported, and the receipt for the report. See one incident log. | Helps assess whether the incident is significant. |
| Management approval | Management approves the measures and oversees them. This cannot be handed over. | Tasks that require approval by the owner, and the dashboard exported as a PDF with your own notes. | Prepares the material for management. |
| Training | Management takes part in the training itself. | Sends awareness as an audit with links to your own training material. See awareness in practice. | Delivers the course or the material. |
Two things the table does not change. .legal does not advise and does not fill in the documentation for you. And management's responsibility under NIS2 stays with management. No platform and no partner can take it over.
NIS2 with a partner
When you switch NIS2 on in .legal, the controls match the source 1:1. Under them sit tasks that say what has to be documented, with practical tips. You choose NIS2 activities from the .legal library, and each one creates tasks with an owner and a due date. That is the structure a partner works inside.
NIS2 with a partner
It is better to say this before anyone books a demo. .legal is a documentation platform. We don't advise, we don't write your policies and we don't fill in the documentation for you. That part belongs to you and, if you want one, a partner.
NIS2 with a partner
Under NIS2 the management body approves the cybersecurity risk-management measures, oversees how they are implemented and takes part in training itself. In Denmark that is section 7 of the NIS2 Act, based on Article 20 of the directive. A partner can prepare the material, but the approval and the management accountability cannot be handed over.
NIS2 with a partner
If you don't have the people in-house, find an implementation partner in our partner directory. We don't recommend a particular one here. You choose the partner that fits how you work, and then you decide how much of the platform they see.
NIS2 with a partner
Onboarding and support are included in every plan. If your risk register, supplier list or policies live in Excel or another system, .legal helps you get them in. There is no self-service import, so we do it with you.
The NIS2 controls match the source 1:1, with tasks underneath that say what has to be documented.
Add a partner as a user at no extra cost, or give them a role you control with Advanced User Management.
A task can require approval by its owner, so decisions are recorded where the work is done.
Choose NIS2 activities from the .legal library, and each one creates tasks with an owner and a due date.
Register NIS2 incidents with the standard template, link them to assets and suppliers, and upload the receipt for the report.
Export the dashboard as a PDF with a title and your own notes for management.
NIS2 with a partner
The work on this page is NIS2 work, task by task.
NIS2
Management approval, risk management, supply chain security and incident handling are all part of NIS2. Split them between you, a partner and the platform.
The NIS2 controls, the templates and the progress in one place.
NIS2 in .legalFind an implementation partner who can advise you and do the implementation work with you.
Find a partnerA recorded demo of working with NIS2 and ISO 27000 tasks in .legal.
Watch the democompanies
users
contracts
processing activities
Bech-Bruun
Mikkel Friis Rossa (Partner)
Fenerum
Rasmus Boutrup (Financial Controller)
Lægeforeningen
Michael Berner (Lawyer)
Molecule Consultancy
Nanna Rodian Christensen (HR & Operational Manager)
Plum Safety
Ulrik Dueholm Beckmann (QC, CM og ESG Lead)
Bech-Bruun
Mikkel Friis Rossa (Partner)
Fenerum
Rasmus Boutrup (Financial Controller)
Lægeforeningen
Michael Berner (Lawyer)
Molecule Consultancy
Nanna Rodian Christensen (HR & Operational Manager)
Plum Safety
Ulrik Dueholm Beckmann (QC, CM og ESG Lead)
Novicell
Julie Oxenvad (Legal Consultant)
Min By Media
Tinna Schultz (HR Manager)
DMJX
Kaspar Rochholz (GDPR Coordinator)
Axel Kaufmann ApS
Julie Lundkvist Andreasen (Lawyer and Head of Costumer Service)
NRGi
Mette Mühlendorph (Compliance Specialist)
Novicell
Julie Oxenvad (Legal Consultant)
Min By Media
Tinna Schultz (HR Manager)
DMJX
Kaspar Rochholz (GDPR Coordinator)
Axel Kaufmann ApS
Julie Lundkvist Andreasen (Lawyer and Head of Costumer Service)
NRGi
Mette Mühlendorph (Compliance Specialist)
Every use case is a real piece of compliance work, told the way it actually runs in the platform. Filter by who you are, what you work with, and which frameworks you answer to.
24 use cases
No use cases match that combination yet. Try removing a filter.
No. .legal is a documentation platform and does not advise or fill in the documentation for you. The platform gives you the structure: NIS2 controls that match the source 1:1, task templates that say what has to be documented, tasks with owners and due dates, and the follow-up. The advice and the implementation work come from you or from an implementation partner, which you can find in the .legal partner directory.
No. Under NIS2 the management body approves the cybersecurity risk-management measures, oversees their implementation and takes part in training. In Denmark this follows from section 7 of the NIS2 Act, based on Article 20 of the directive. A partner can prepare the material and advise, and .legal can document the approvals with tasks that require approval and a dashboard exported as a PDF with notes. The responsibility still stays with management.
What NIS2 requires of management trainingNot for ordinary access. An external partner, such as a consultant or an auditor, can be added as a user in .legal with the same access as your own users at no extra cost. If you want to decide exactly what the partner can see and edit, or give an auditor a role that can only read, that requires Advanced User Management.
You do, together with your partner or your auditor. The task templates in .legal describe what has to be documented and give practical tips, and a task can require that documentation is attached and that the owner approves it before it is closed. Whether the evidence is good enough is not something the platform decides.
Yes. Onboarding and support are included in every .legal plan, and .legal helps you bring existing data in from Excel or another system. There is no self-service import. Risk assessments are only imported directly when that can be done without interpreting them on your behalf. Otherwise you agree with .legal how they are brought in.
From spreadsheets to one platform