Skip to content

Critical assets under NIS2

Risk-assess your critical assets under NIS2

"We don't know which systems are critical, and the risk assessment lives in a spreadsheet." Map your assets, flag the ones your services depend on, and assess them against NIS2 scenarios in Enterprise Risk Management, so management gets a report it can read.
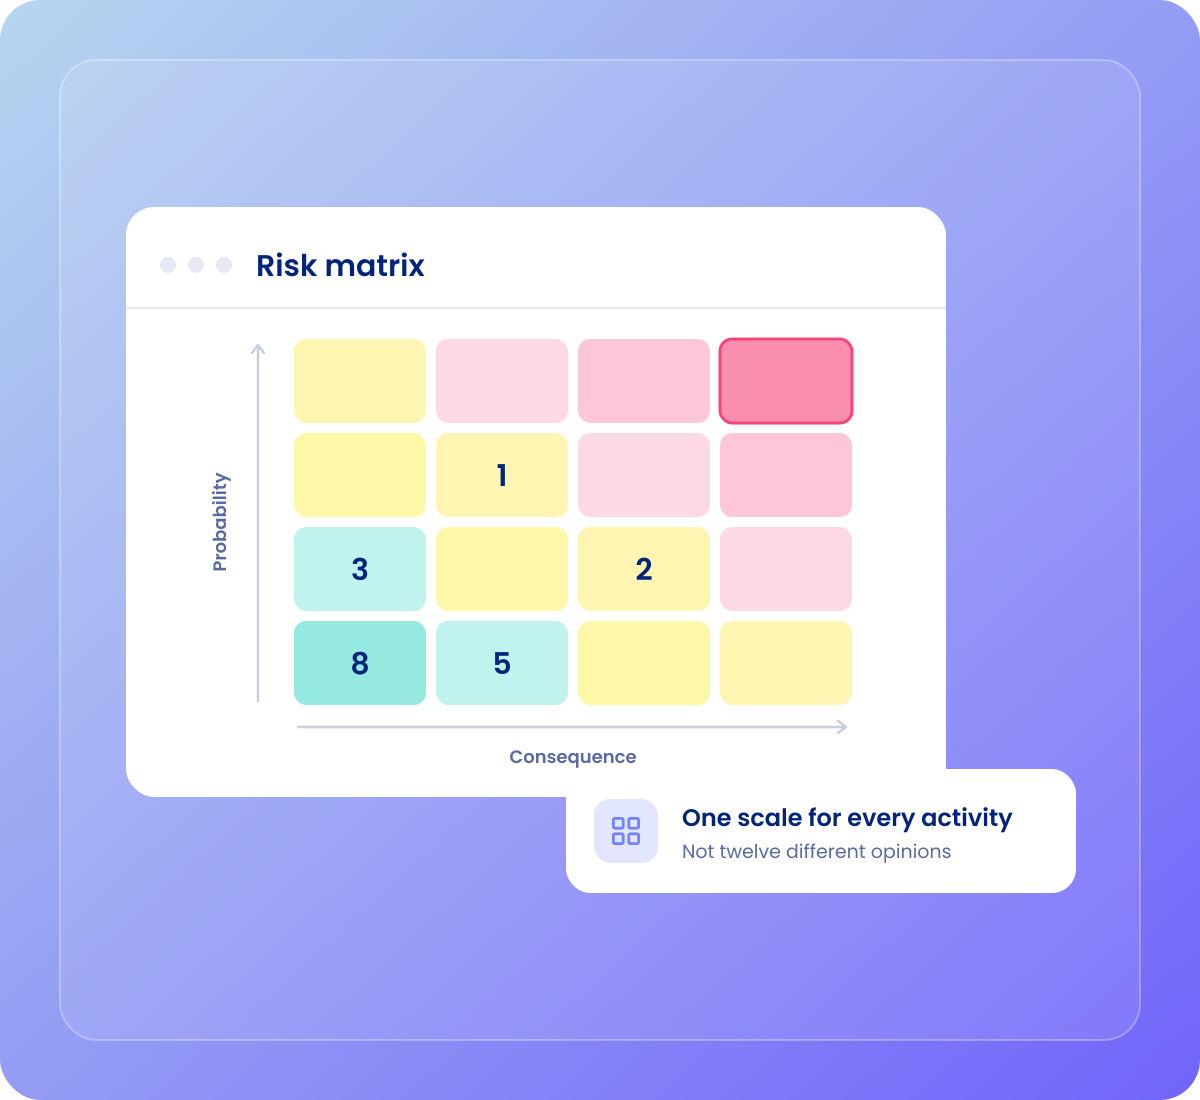
A risk matrix in .legal with probability and consequence, where most assessments sit in the low corner and the highest cell is outlined
+400 companies use .legal
Region Sjælland
Aarhus Universitet
aj_vaccines_logo
Realdania
Right People
IO Gates
PLO
Finans Danmark
geia-food
Evida
Klasselotteriet
NRGI1
BLUE WATER SHIPPING
Karnov
Ingvard Christensen
VP Securities
AH Industries
Lægeforeningen
InMobile
AK Nygart
DEIF
DMJX
Axel logo
qUINT Logo
KAUFMANN (1)
SMILfonden-logo
kurhotel_skodsborg
nemlig.com
Molecule Consultancy
Novicell
The asset list in .legal filtered on operation critical: a hosting database, a VPN gateway, a customer portal and a payroll system, each with its supplier and a NIS2 risk level from low to high

Critical assets

Meridian knows which systems its services stand on

Jonas Berg is CISO at Meridian Nordic, an energy group with NIS2 obligations. When the board asked which systems the business could not run without, the answer sat in three people's heads and a spreadsheet nobody trusted. Now every asset is mapped in .legal, the ones the services depend on are flagged as critical, and those are assessed against NIS2 scenarios in a risk area of their own.

  • An asset is flagged as critical when the services Meridian delivers depend on it.
  • The asset list filters on critical, and on any other field, custom fields included.
  • The critical assets are added to the NIS2 risk area by hand, and assessed in bulk.
  • The management report goes to the board as a PDF, with a comment on it.

  • Flag what is critical

    Mark an asset as critical when the services you deliver depend on it. It is your call, made asset by asset.

  • A NIS2 risk area

    Create a risk area for NIS2 in Enterprise Risk Management and import scenarios, consequences and security measures from the catalogue.

  • Assess in bulk

    Assess and mitigate one at a time, or in bulk across many assets and scenarios.

  • A report for management

    Export the management report as a PDF, with your own comment on it.

Five spreadsheets of different sizes scattered with no connection between them

Critical assets

A list of systems is not a risk assessment

Most organisations have a list of their systems somewhere. The trouble starts when NIS2 asks for risk management on the systems you deliver your services with, and the list can't tell you which ones those are.

  • Critical assets and suppliers are not mapped in one place, even though supply chain security is one of the minimum measures.
  • The risk assessment lives in a spreadsheet with no link to the controls.
  • The board asks "how far are we?", and the answer is put together by hand.
The Microsoft 365 asset in .legal with Microsoft Corporation as supplier, marked as operation critical, ISO 27001 certified and with AI features in use

Critical assets

Map the assets, then flag what your services depend on

Start with the assets: the IT systems, OT and other resources you deliver your services with. NIS2 lists asset management among the minimum measures, and you can't assess what you haven't mapped. If your assets already sit in a spreadsheet, .legal helps you with the import.

  • Flag an asset as critical when the services your organisation delivers depend on it.
  • Filter the asset list on critical, or on any of the asset's fields, custom fields included.
  • Link assets to incidents and processes. With Information and Cyber Security, associated assets also show dependencies and value chains, such as front end, API and database.
The NIS2 risk area in .legal with a 1–4 scale, a risk appetite of 3, four levels from very low to high and a matrix

Critical assets

Give NIS2 a risk area of its own

In Enterprise Risk Management you create a risk area for NIS2. The scenarios don't have to start from a blank page. You import risk scenarios, consequences and security measures from the .legal catalogue, which is built around GDPR, NIS2 and AI, and adjust them to fit how you work.

  • The catalogue is a starting point, not an answer. Everything you import can be edited afterwards.
  • For what the assessment itself has to cover, read our guide to NIS2 risk assessment.
The Operational tab of the NIS2 risk area in .legal with a customer portal asset, a supplier, a process and a processing activity, each with risk before and after mitigation

Critical assets

Choose the critical assets, and assess them in bulk

The assets become entities in the NIS2 risk area. You choose which entities the area covers, and nothing is attached automatically, so a critical asset is in the assessment because somebody put it there. Then you assess them against the scenarios, one at a time or in bulk across many assets and scenarios.

  • Filter the asset list on critical first, then add those assets to the risk area yourselves.
  • Mitigation works the same way: one at a time, or in bulk.
The management report in .legal with exposure now at DKK 4.2m, DKK 1.1m after open plans, plans' cost DKK 350,000, 61 of 61 entities assessed and 7 risks above appetite

Critical assets

A report management can read

Under NIS2 the management body approves the risk-management measures and oversees how they are implemented. That is easier with a report than with a spreadsheet. Export the management report from Enterprise Risk Management as a PDF, and add a comment so the numbers arrive with their context.

  • The PDF carries a comment from the person who exported it.
  • The report covers the risk work. It is not an overall verdict on whether you comply with NIS2.
A tall register panel with rows, where a new row is added by hand with a pen, and nothing on the panel counts down or scans

Critical assets

What you still decide yourselves

We supply the structure, the catalogue and the report. Some judgements stay with you, and it is better to say so before anyone books a demo. Whether you are an essential entity, an important one or not covered at all is one of them.

  • Critical assets are chosen by hand. Nothing adds them to the NIS2 risk assessment automatically. You filter the list on critical and add them yourselves.
  • The platform doesn't decide whether you are covered by NIS2, and it doesn't report incidents to the authorities.
  • Enterprise Risk Management is part of the Enterprise offer and is priced in the quote. It has no list price.
.legal in practice

Features for critical asset risk assessment

Critical assets, flagged

Mark an asset as critical when the services your organisation delivers depend on it, then filter the asset list on it, or on any other field.

A NIS2 risk area (Enterprise)

Create a risk area for NIS2 in Enterprise Risk Management, which is part of the Enterprise offer and priced in the quote.

A catalogue to start from

Import risk scenarios, consequences and security measures from the .legal catalogue, built around GDPR, NIS2 and AI, and adjust them afterwards.

Assets as entities, chosen by you

You choose which assets the risk area covers. Nothing is attached automatically, so the decision stays with a person.

Assess and mitigate in bulk

Assess and mitigate one at a time, or in bulk across many assets and scenarios at once.

A PDF for management

Export the management report as a PDF, with a comment from the person exporting it.

Critical assets

Frameworks this covers

One asset list, and the two frameworks it carries most weight for.

  • icon-framework-NIS2

    NIS2

    Risk analysis, supply chain security and asset management are among the minimum measures. Map the assets your services depend on and assess them in a NIS2 risk area.

    Learn about NIS2
  • icon-framework-ISO

    ISO 27001

    ISO 27001 also expects you to know your assets and assess the risks to them, so the same asset list serves both frameworks.

    Learn about ISO 27001
.legal compliance platform

Risk-assess your critical assets with...

Do you need to risk-assess your critical assets under NIS2? We recommend the following modules for that task.

Information and Cyber Security

Where the assets and their critical flag live. Associated assets, which show dependencies and value chains, require Information and Cyber Security.

Explore Information and Cyber Security

Enterprise Risk Management

The NIS2 risk area, the scenario catalogue, bulk assessment and the management report as a PDF. Part of the Enterprise offer, priced in the quote.

Explore Enterprise Risk Management

NIS2 mapping and risk assessment demo

A recorded video demo of mapping your NIS2 assets in .legal and assessing the risks to them.

Watch the demo

Our Customers

+400

companies

+11.000

users

+79.000

contracts

+14.000

processing activities

Mikkel Friis

Bech-Bruun

Mikkel Friis Rossa (Partner)

.legal's team has consistently demonstrated a commitment to innovation while being responsive to the needs of our mutual clients.

Rasmus-boutrup-fenerum

Fenerum

Rasmus Boutrup (Financial Controller)

Case Study
With .legal, we've gained a simpler and more manageable solution that better suits our needs
Michael Berner 1

Lægeforeningen

Michael Berner (Lawyer)

.legal has been the right choice for us. .legal are professional and welcoming with skilled employees.
Nanna Rodian Christensen

Molecule Consultancy

Nanna Rodian Christensen (HR & Operational Manager)

Case Study
Firstly, it means that not all the work is in one place (me), and secondly, that the understanding of GDPR is implemented throughout the organisation.
ulrikdueholmbeckmann

Plum Safety

Ulrik Dueholm Beckmann (QC, CM og ESG Lead)

Case Study
From .legal, we experience an incredibly high degree of flexibility and willingness to adapt features to our local needs.
julie-oxenvad-novicell

Novicell

Julie Oxenvad (Legal Consultant)

Case Study
We are satisfied with the switch to .legal – it has strengthened our compliance work, made processes easier to manage and more transparent, and improved cross-team collaboration
Tinna Schultz

Min By Media

Tinna Schultz (HR Manager)

Case Study
It just works! It is so easy and user-friendly, and the overview of processing activities is brilliant.
ansat_Kaspar_Rochholz_005

DMJX

Kaspar Rochholz (GDPR Coordinator)

Case Study
.legal has really understood what it means to create a user-friendly and efficient solution. Privacy is an attractive product compared to price and functionality.
Profile-picture1

Axel Kaufmann ApS

Julie Lundkvist Andreasen (Lawyer and Head of Costumer Service)

Case Study
.legal continuously update the platform to ensure their customers always remain compliant. In our view, any other choice would be a downgrade.

NRGi

Mette Mühlendorph (Compliance Specialist)

Case Study
The implementation of .legal has made a difference in the way we handle compliance. The system has created structure and overview, which has had concrete benefits.
Use cases

Find the job you need done

Every use case is a real piece of compliance work, told the way it actually runs in the platform. Filter by who you are, what you work with, and which frameworks you answer to.

Book demo

23 use cases

Compliance & GRC lead

Run awareness training that reaches every colleague

Send out training and policies, chase the stragglers automatically, and prove every colleague completed it. You bring the material, we run the rails.
See awareness training
Compliance & GRC lead

Manage compliance across a group of companies

Run every company in the group from one platform, document once at group level, and still report entity by entity. Delivered by the Group Companies add-on.
See group compliance
Legal counsel

Run due diligence on your vendors

Classify a vendor on your own criteria, get the answers and documents you need with no login for them, and move the approved ones straight into contracts.
See vendor due diligence
Compliance & GRC lead

Multi-framework compliance: do the work once

Do a control once and it counts across every framework it maps to, with a simulated score on the ones you haven't started yet.
See multi-framework compliance
CISO & IT security

Get NIS2-ready without starting from scratch

Build on the ISO 27001 work you've already done, switch NIS2 on, and let a simulated score show how far ahead you already are.
See NIS2 readiness
DPO

From twelve spreadsheets to one record of processing

Your GDPR documentation already exists, it just lives in spreadsheets. Export what you have and we structure it in .legal for you, typically inside two weeks.
See the move off spreadsheets
Compliance & GRC lead

Build one risk register for the whole organisation

One register across GDPR, NIS2, AI and information security, where each risk area keeps its own matrix, scale and appetite. Delivered by the Enterprise Risk Management add-on.
See the risk register
Executive & board

Give the board a risk picture it can act on

One management report across every risk area: entities assessed, risks above appetite, exposure now and once the open plans are done. Export it with your own comment on it.
See board risk reporting

Frequently asked questions about critical asset risk assessment

What is a critical asset under NIS2?

The NIS2 rules don't give you a ready-made list of critical assets. They require appropriate and proportionate measures to manage the risks to the network and information systems you use for your operations or to deliver your services, and asset management is one of the minimum measures. In practice a critical asset is a system or other resource your services depend on. In .legal you mark an asset as critical when the services your organisation delivers depend on it, and that judgement is yours to make.

Do all assets have to be risk-assessed?

Not necessarily in the same depth. NIS2 asks for measures that are appropriate and proportionate, so a sensible place to start is the assets your services depend on, and you widen the scope from there. In .legal you choose which assets the NIS2 risk area in Enterprise Risk Management covers, and you can assess them one at a time or in bulk across many assets and scenarios.

What a risk assessment involves

Are critical assets added to the risk assessment automatically?

No. Marking an asset as critical does not add it to the NIS2 risk assessment. You filter the asset list on critical and add the assets to the risk area yourselves. In Enterprise Risk Management you choose which entities each risk area covers, and nothing is attached automatically. That keeps the decision with a person, and it also means somebody has to make it.

Can the report be used with management?

Yes, that is what it is for. The management report in Enterprise Risk Management exports as a PDF, and the person exporting it can add a comment. Under NIS2 the management body approves the risk-management measures and oversees their implementation, so a report it can read is a practical way to show the work. The report covers risk only and is not an overall verdict on NIS2 compliance.

Does .legal decide whether we are covered by NIS2?

No. Whether you are covered, and whether you are an essential or an important entity, is your own assessment, and .legal does not make it for you. The platform documents the work once you know: the assets, the critical ones, the NIS2 risk area and the management report. Enterprise Risk Management, where the risk area and the report live, is part of the Enterprise offer and priced in the quote.

What an important entity is

Still unsure?

Ask Johannes directly, he runs most demos personally

Book him here
+400 companies use .legal
Region Sjælland
Aarhus Universitet
aj_vaccines_logo
Realdania
Right People
IO Gates
PLO
Finans Danmark
geia-food
Evida
Klasselotteriet
NRGI1
BLUE WATER SHIPPING
Karnov
Ingvard Christensen
VP Securities
AH Industries
Lægeforeningen
InMobile
AK Nygart
DEIF
DMJX
Axel logo
qUINT Logo
KAUFMANN (1)
SMILfonden-logo
kurhotel_skodsborg
nemlig.com
Molecule Consultancy
Novicell